Skip to content

[No QA] [Payment due @huult] Stop routing group workspace members to the reports upgrade screen - #101465

Merged
francoisl merged 11 commits into
mainfrom
claude-reportUpgradeHydrationGuard
Oct 14, 2026
Merged

francoisl merged 11 commits into
mainfrom
claude-reportUpgradeHydrationGuard

Conversation

@MelvinBot

@MelvinBot MelvinBot commented Sep 17, 2026 •

Copy link
Copy Markdown
Contributor

Explanation of Change

Members of a group workspace were sometimes shown the "Reports are available on the Collect plan, starting at $5 per member per month" upgrade screen, even though their workspace already supports reports. This is not a plan gate — reports has no requiredPlan and is not in SUBMIT_FEATURE_IDS. The screen is the App's "you have no eligible group workspace" prompt, and UpgradeIntro is rendered without a policyID, so it always shows the hardcoded Collect wording no matter what plan the user is actually on.

usePolicyForMovingExpenses gates that prompt, and it treated "I could not resolve a policy" as "this user has no workspace" in three ways that are wrong for a real member:

  1. No hydration guard. The policy collection read at the top of the hook discarded its load status, so the moment the collection read back empty — including during Onyx cold start — the hook returned shouldNavigateToUpgradePath: true. useCreateReport already guards the identical situation about 40 lines away, with a comment describing this exact bug. This change reads the load status off the same useOnyx call (so the value and the status always come from the same source, including when the search-snapshot redirect is in play) and no longer claims "no workspace" before we know.

  2. The active-workspace fallback was unreachable. The activePolicy fallback sat below the unconditional early return, so a fully loaded, valid active workspace could never rescue the user. It now runs before the upgrade path. It is validated with isPolicyValidForMovingExpenses rather than the looser check the old fallback used, so an active workspace is only used when it is genuinely a valid destination — this cannot select something the old code would have rejected.

  3. EmptySearchView dropped the login. getGroupPoliciesWhereReportCanBeCreated was called without currentUserLogin. getPolicyRole returns early when there is no login, which makes its employeeList[login].role fallback dead code, so any policy that carries the member's role only in employeeList was filtered out and the user looked workspace-less. This was the only one of seven call sites that omitted the login; the FAB, Search router, workspace selector, and navigation guard all pass it.

One more ordering fix came out of this: the isUnreportedManagedCardTransaction branch never depends on a locally resolved policy — it deliberately returns an empty policyID so the backend auto-selects — but it sat below the early return, so that flow also hit the upgrade screen whenever no policy resolved. It is now answered first.

Update — review feedback applied. Two follow-ups from the automated review are now in:

  1. The role check is login-aware. isPolicyMemberByRole resolved the role from policy.role only, which the backend populates just for the user's default/active workspace. It now goes through getPolicyRole(policy, login), so a workspace whose role arrives only in employeeList is accepted here the same way getGroupPoliciesWhereReportCanBeCreated already accepts it. Without this, the active-workspace fallback in item 2 could not rescue exactly the members it was added for.

  2. The hook exposes arePoliciesLoaded. During the hydration window shouldNavigateToUpgradePath: false means "I don't know yet", not "this user has an eligible policy". Every consumer that only navigates already handles an unresolved policy — they fall through to a workspace selector or report picker, which creates nothing. But SearchTransactionsChangeReport mutates: it would have created a report with an undefined policy and moved the selected transactions into it. That one call site now no-ops while the collection loads, matching useCreateReport.

Also worth noting: isLoadingOnyxValue only reflects the local cache read, not network hydration. The guard closes the cold-start window; the active-workspace fallback in item 2 is what covers the longer "response has not landed yet" window.

Fixed Issues

$ https://github.com/Expensify/Expensify/issues/681029
PROPOSAL: https://github.com/Expensify/Expensify/issues/681029#issuecomment-5702368350

AI Tests

All required local AI tests for these files now pass against main:

  • npm run typecheck — passed. The earlier CI failure was stale-branch drift in tests/unit/ModifiedExpenseMessageTest.ts, a file this PR does not touch; merging main fixed it.
  • npm run lint-changed — passed
  • npm run react-compiler-compliance-check check on the two changed source files — passed
  • npm run spell-changed — passed, 0 issues across 5 files
  • npm run fmt (oxfmt) — clean
  • npm test tests/unit/hooks/usePolicyForMovingExpenses.test.tsx tests/ui/components/SearchActionsBarCreateButtonTest.tsx — 15 passed

New unit tests in tests/unit/hooks/usePolicyForMovingExpenses.test.tsx cover the cold-start hydration guard, the employeeList role fallback, and the managed-card-transaction path. The employeeList case was checked against the pre-fix policy.role-only code and fails there, so it is a real regression test rather than a passing tautology.

Not verified in a browser: the cold-start race itself. Driving a real page reload or app relaunch was outside what the automated runs on this PR could do, so that window still wants a manual pass on top of the unit test.

Tests

  1. Sign in to staging with a test account that belongs to one Collect or Control workspace.

  2. Open the workspace's Members page to load its member list.

  3. Open Search → Reports and let it finish loading.

  4. In Chrome DevTools → Network, select Offline.

  5. In the console, run:

    const login = (await Onyx.get('session')).email;
    const policies = await Onyx.get('policy_');
    
    const [key, policy] = Object.entries(policies).find(
        ([, p]) => ['team', 'corporate'].includes(p?.type)
    );
    
    if (!policy.employeeList?.[login]?.role) {
        throw new Error('Open the workspace Members page to load your membership first.');
    }
    
    window.reportReproBackup = {key, policy: structuredClone(policy)};
    
    const {role, ...partialPolicy} = policy;
    await Onyx.set(key, partialPolicy);
  6. Without reloading, select Create → Create report in the Search header.

  7. Verify the result:

    • Before the fix: the Collect upgrade screen appears despite the account's workspace membership.
    • With the fix: the app recognizes the membership and continues through the normal report flow.
  8. Before reloading or going online, restore the original data:

    await Onyx.set(
        window.reportReproBackup.key,
        window.reportReproBackup.policy
    );
    delete window.reportReproBackup;
  9. In DevTools → Network, select No throttling.

  • Verify that no errors appear in the JS console

Offline tests

QA Steps

// TODO: The human co-author must fill out the QA tests you ran before marking this PR as "ready for review".
// Please describe what QA needs to do to validate your changes and what areas do they need to test for regressions.

  • Verify that no errors appear in the JS console

PR Author Checklist

  • I linked the correct issue in the ### Fixed Issues section above
  • I wrote clear testing steps that cover the changes made in this PR
    • I added steps for local testing in the Tests section
    • I added steps for the expected offline behavior in the Offline steps section
    • I added steps for Staging and/or Production testing in the QA steps section
    • I added steps to cover failure scenarios (i.e. verify an input displays the correct error message if the entered data is not correct)
    • I turned off my network connection and tested it while offline to ensure it matches the expected behavior (i.e. verify the default avatar icon is displayed if app is offline)
    • I tested this PR with a High Traffic account against the staging or production API to ensure there are no regressions (e.g. long loading states that impact usability).
  • I included screenshots or videos for tests on all platforms
  • I ran the tests on all platforms & verified they passed on:
    • Android: Native
    • Android: mWeb Chrome
    • iOS: Native
    • iOS: mWeb Safari
    • MacOS: Chrome / Safari
  • I verified there are no console errors (if there's a console error not related to the PR, report it or open an issue for it to be fixed)
  • I followed proper code patterns (see Reviewing the code)
    • I verified that comments were added to code that is not self explanatory
    • I verified that any new or modified comments were clear, correct English, and explained "why" the code was doing something instead of only explaining "what" the code was doing.
    • I verified any copy / text that was added to the app is grammatically correct in English. It adheres to proper capitalization guidelines (note: only the first word of header/labels should be capitalized), and is either coming verbatim from figma or has been approved by marketing (in order to get marketing approval, ask the Bug Zero team member to add the Waiting for copy label to the issue)
  • If a new code pattern is added I verified it was agreed to be used by multiple Expensify engineers
  • I followed the guidelines as stated in the Review Guidelines
  • I tested other components that can be impacted by my changes (i.e. if the PR modifies a shared library or component like Avatar, I verified the components using Avatar are working as expected)
  • If a new CSS style is added I verified that:
    • A similar style doesn't already exist
    • The style can't be created with an existing StyleUtils function (i.e. StyleUtils.getBackgroundAndBorderStyle(theme.componentBG))
  • If new assets were added or existing ones were modified, I verified that:
    • The assets are optimized and compressed (for SVG files, run npm run compress-svg)
    • The assets load correctly across all supported platforms.
  • If the PR modifies code that runs when editing or sending messages, I tested and verified there is no unexpected behavior for all supported markdown - URLs, single line code, code blocks, quotes, headings, bold, strikethrough, and italic.
  • If the PR modifies a generic component, I tested and verified that those changes do not break usages of that component in the rest of the App (i.e. if a shared library or component like Avatar is modified, I verified that Avatar is working as expected in all cases)
  • If the PR modifies a component related to any of the existing Storybook stories, I tested and verified all stories for that component are still working as expected.
  • If the PR modifies a component or page that can be accessed by a direct deeplink, I verified that the code functions as expected when the deeplink is used - from a logged in and logged out account.
  • If the PR modifies the UI (e.g. new buttons, new UI components, changing the padding/spacing/sizing, moving components, etc) or modifies the form input styles:
    • I verified that all the inputs inside a form are aligned with each other.
    • I added Design label and/or tagged @Expensify/design so the design team can review the changes.
  • I added unit tests for any new feature or bug fix in this PR to help automatically prevent regressions in this user flow.
  • If the main branch was merged into this PR after a review, I tested again and verified the outcome was still expected according to the Test steps.

Screenshots/Videos

Android: Native
Android: mWeb Chrome
iOS: Native
iOS: mWeb Safari
MacOS: Chrome / Safari

Guard the upgrade path on policy hydration, let a valid active workspace
rescue the user before the upgrade early return, and pass the current
user login so the employeeList role fallback is reachable.

Co-authored-by: MitchExpensify <MitchExpensify@users.noreply.github.com>
@MelvinBot
MelvinBot requested a review from a team September 17, 2026 20:20
@melvin-bot melvin-bot Bot added Melvin-Test-Android Melvin-Test-Web Triggers Melvin to run the testing steps of the PR on web labels Sep 17, 2026
@codecov

codecov Bot commented Sep 17, 2026 •

Copy link
Copy Markdown

Codecov Report

✅ Changes either increased or maintained existing code coverage, great job!

Files with missing lines Coverage Δ
src/pages/Search/EmptySearchView.tsx 74.82% <100.00%> (ø)
src/hooks/usePolicyForMovingExpenses.ts 96.49% <88.23%> (+0.06%) ⬆️
...rc/pages/Search/SearchTransactionsChangeReport.tsx 0.00% <0.00%> (ø)
... and 9 files with indirect coverage changes

@MelvinBot

MelvinBot commented Sep 17, 2026 •

Copy link
Copy Markdown
Contributor Author

🤖 Android test steps verification results: ⚠️ partial

This PR has no documented testing steps — the Tests and QA Steps sections are still // TODO placeholders — so I derived the test cases from the Explanation of Change and ran those instead. On a group-workspace member on the Collect trial, the Reports tab and the FAB → Create report flow both behaved normally, with no "Reports are available on the Collect plan, starting at $5 per member per month" upgrade screen anywhere, and no JS or console errors. One derived case (the cold-start hydration race) could not be run because relaunching the app is outside what this session is allowed to do.

The handed-off account had no workspaces, so I created a group workspace first — it came up on a Collect free trial, which is the account shape the bug affects.

Draft report created after tapping Create report, no paywall

Step Status
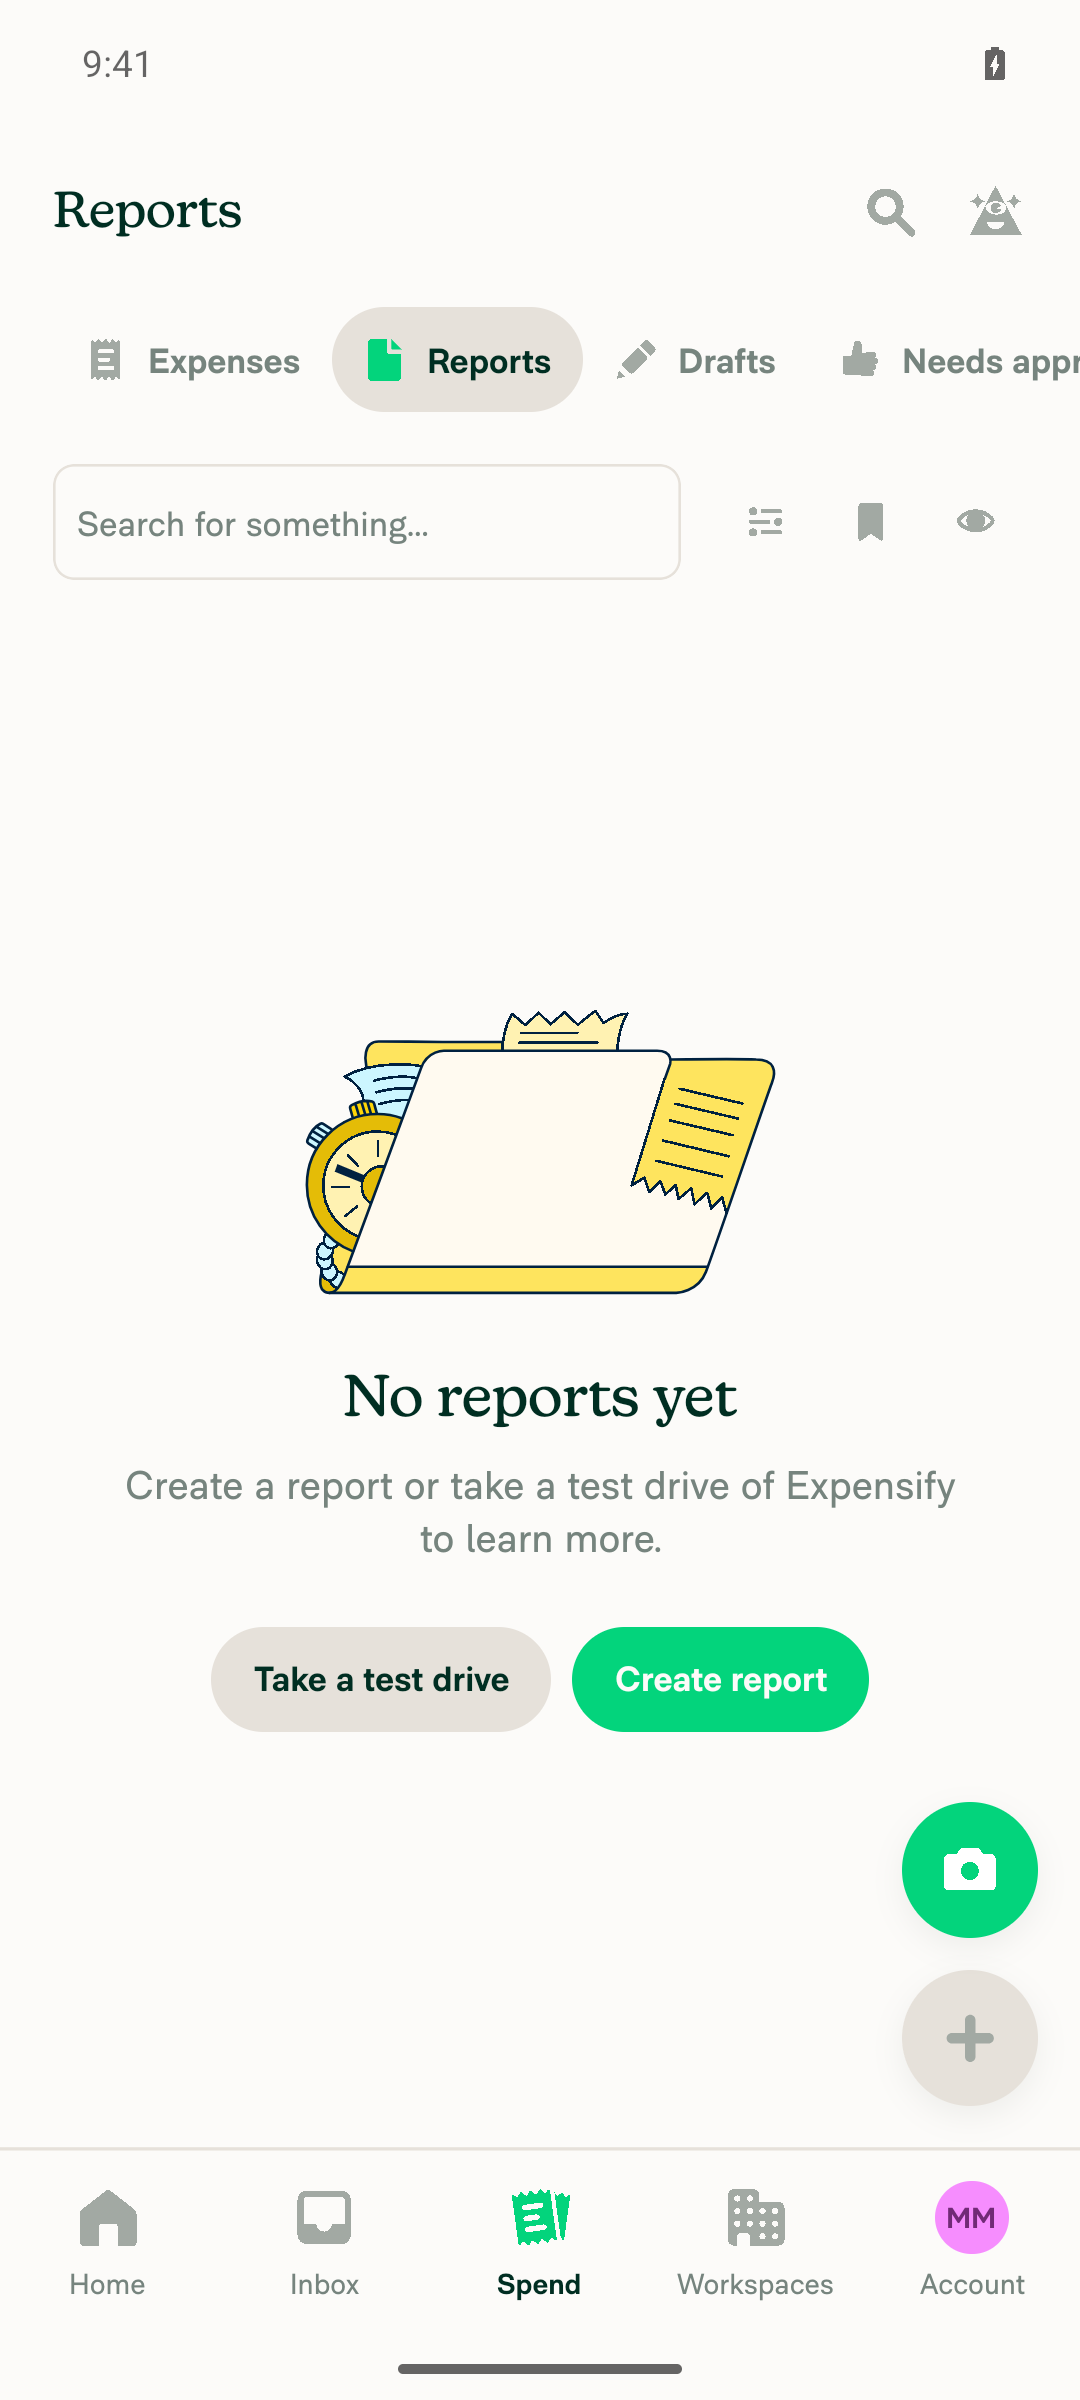
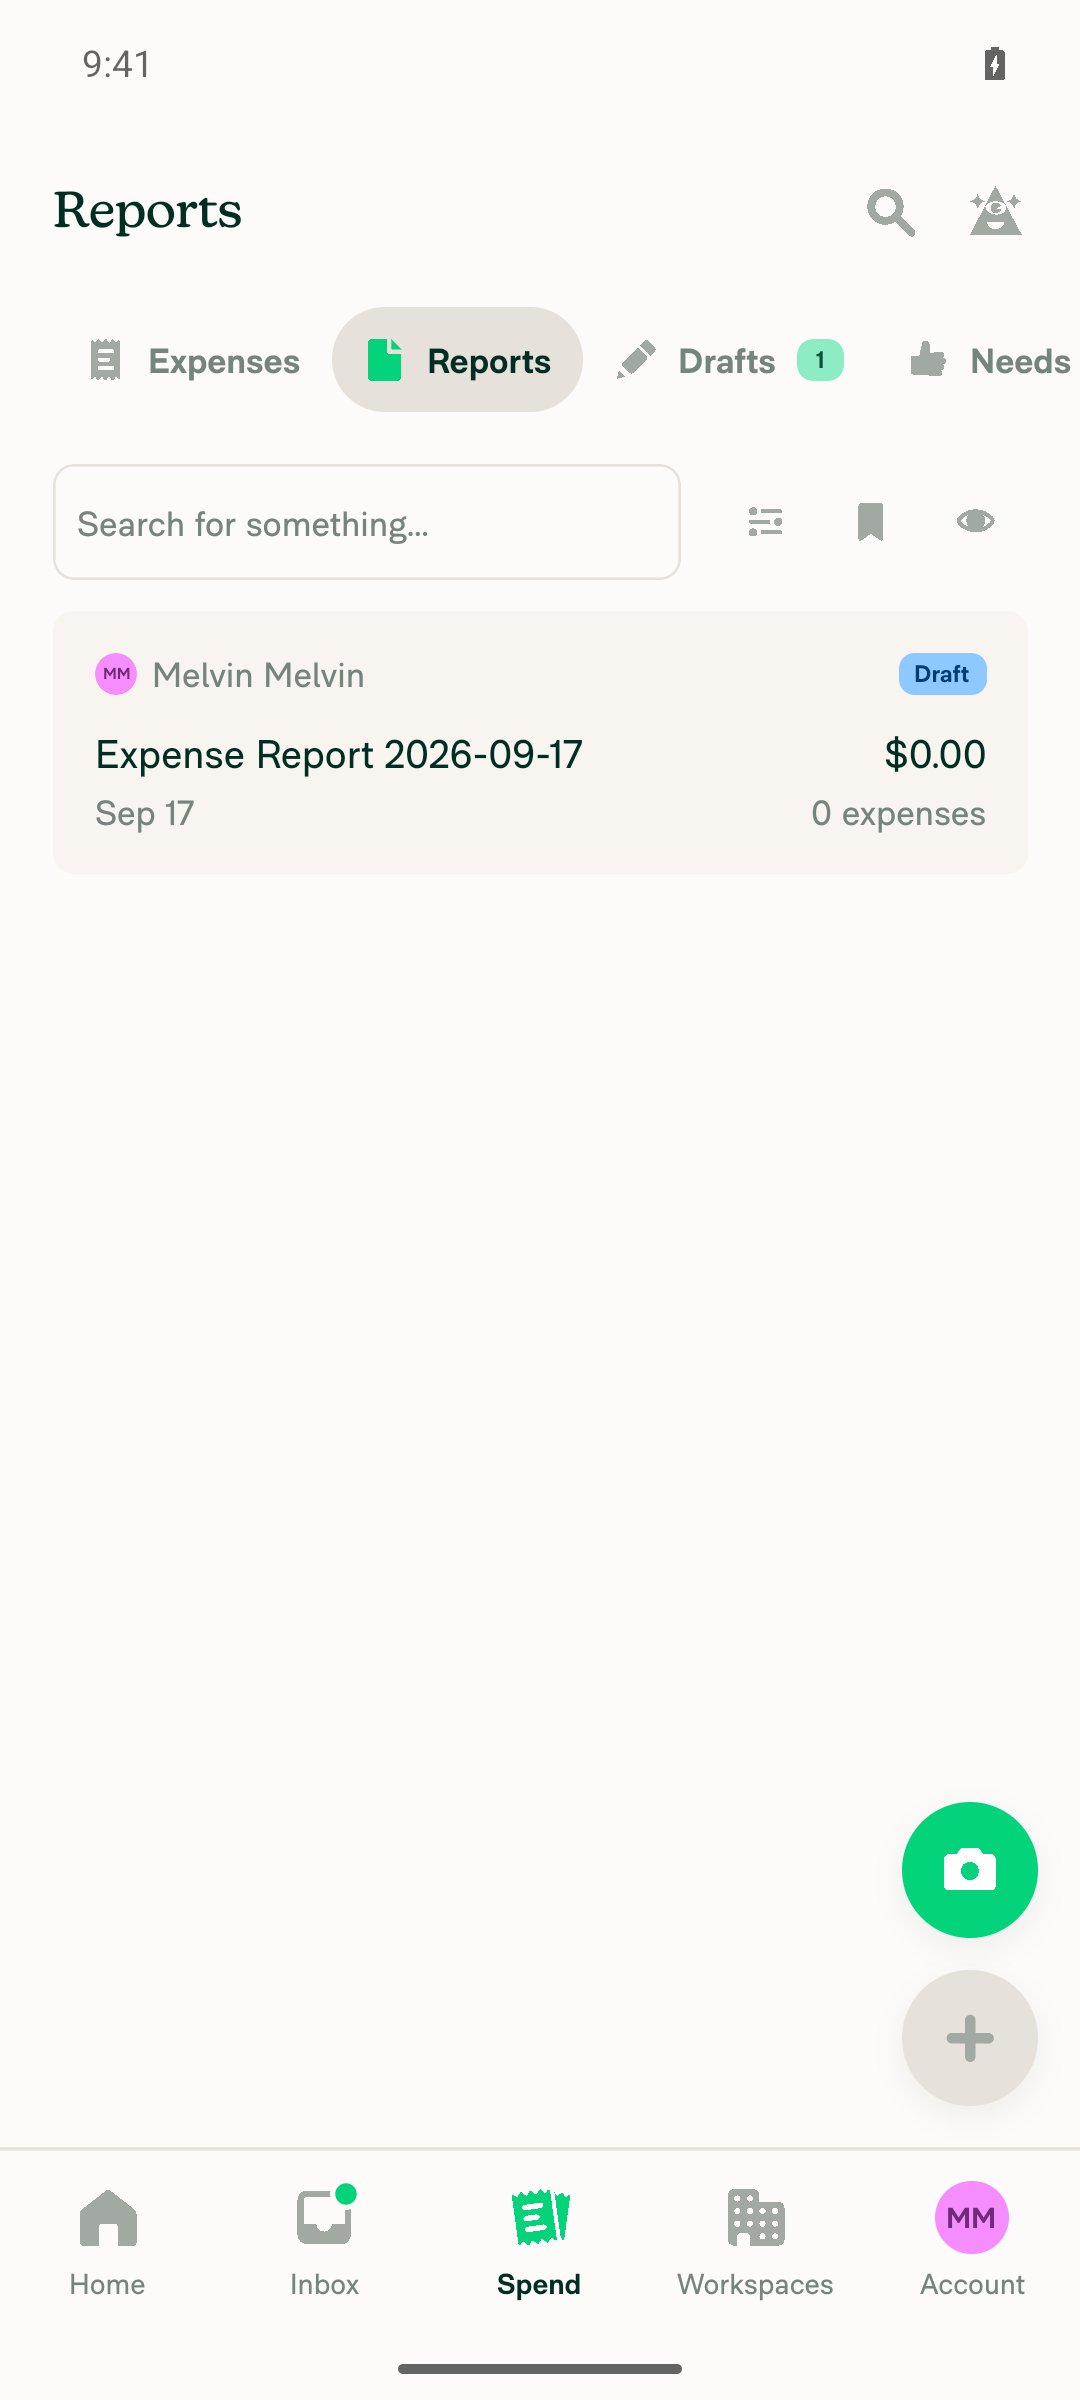
VERIFY 1: Search > Reports shows the normal state, not the Collect plan upgrade screenReports tab first showed the standard "No reports yet / Create a report or take a test drive" empty state, and after creating a draft report it showed the real report list ("Expense Report 2026-09-17", $0.00, 0 expenses). A visibility check for the exact paywall string "Reports are available on the Collect plan, starting at $5 per member per month" found no matching element on this screen.
Reports tab showing normal empty state, no Collect-plan paywall
Reports tab showing the created draft report in the list, no paywall
✅
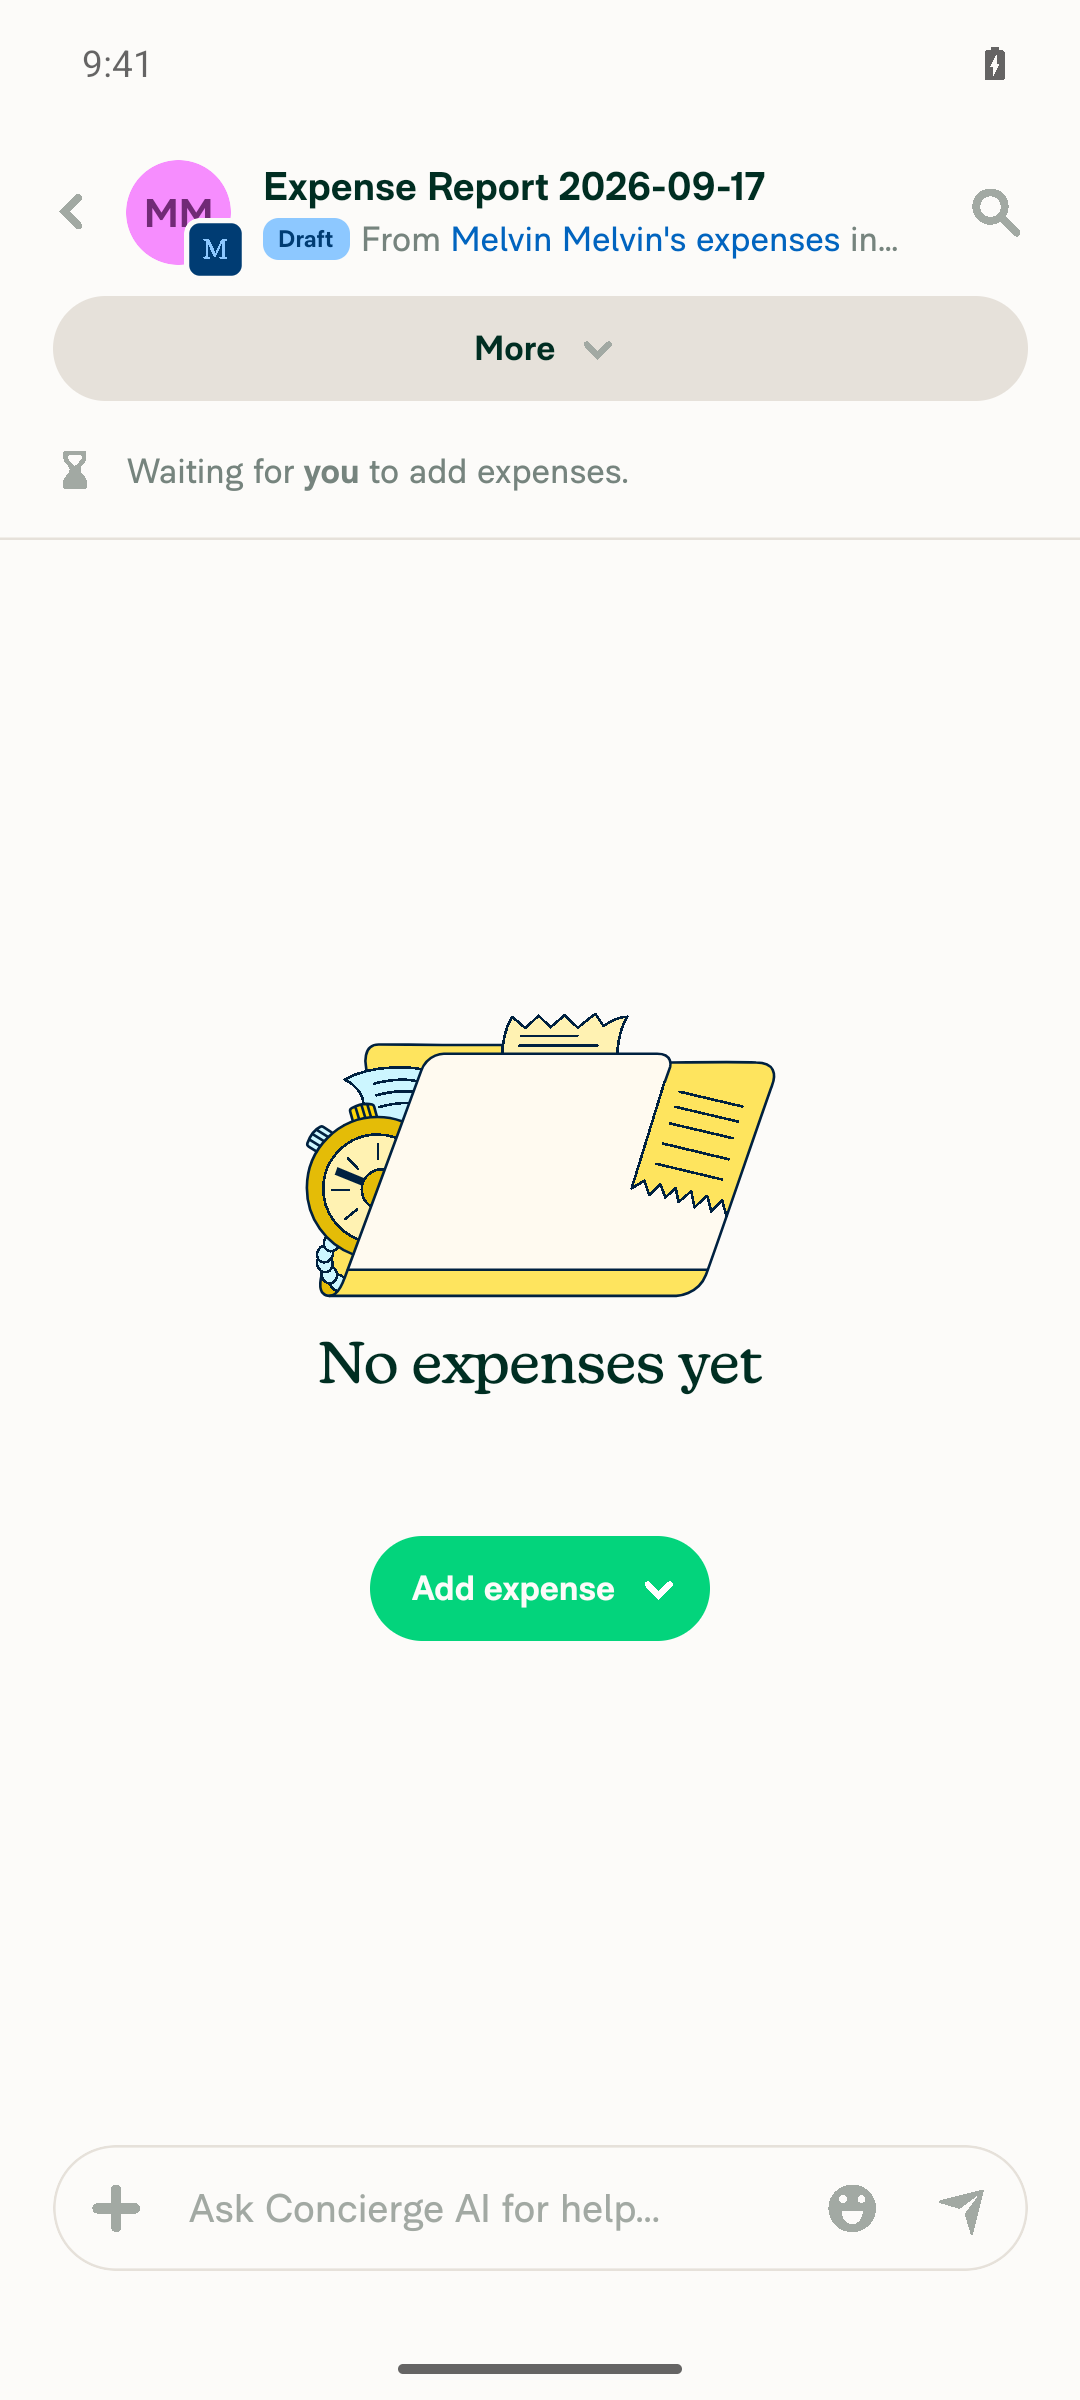
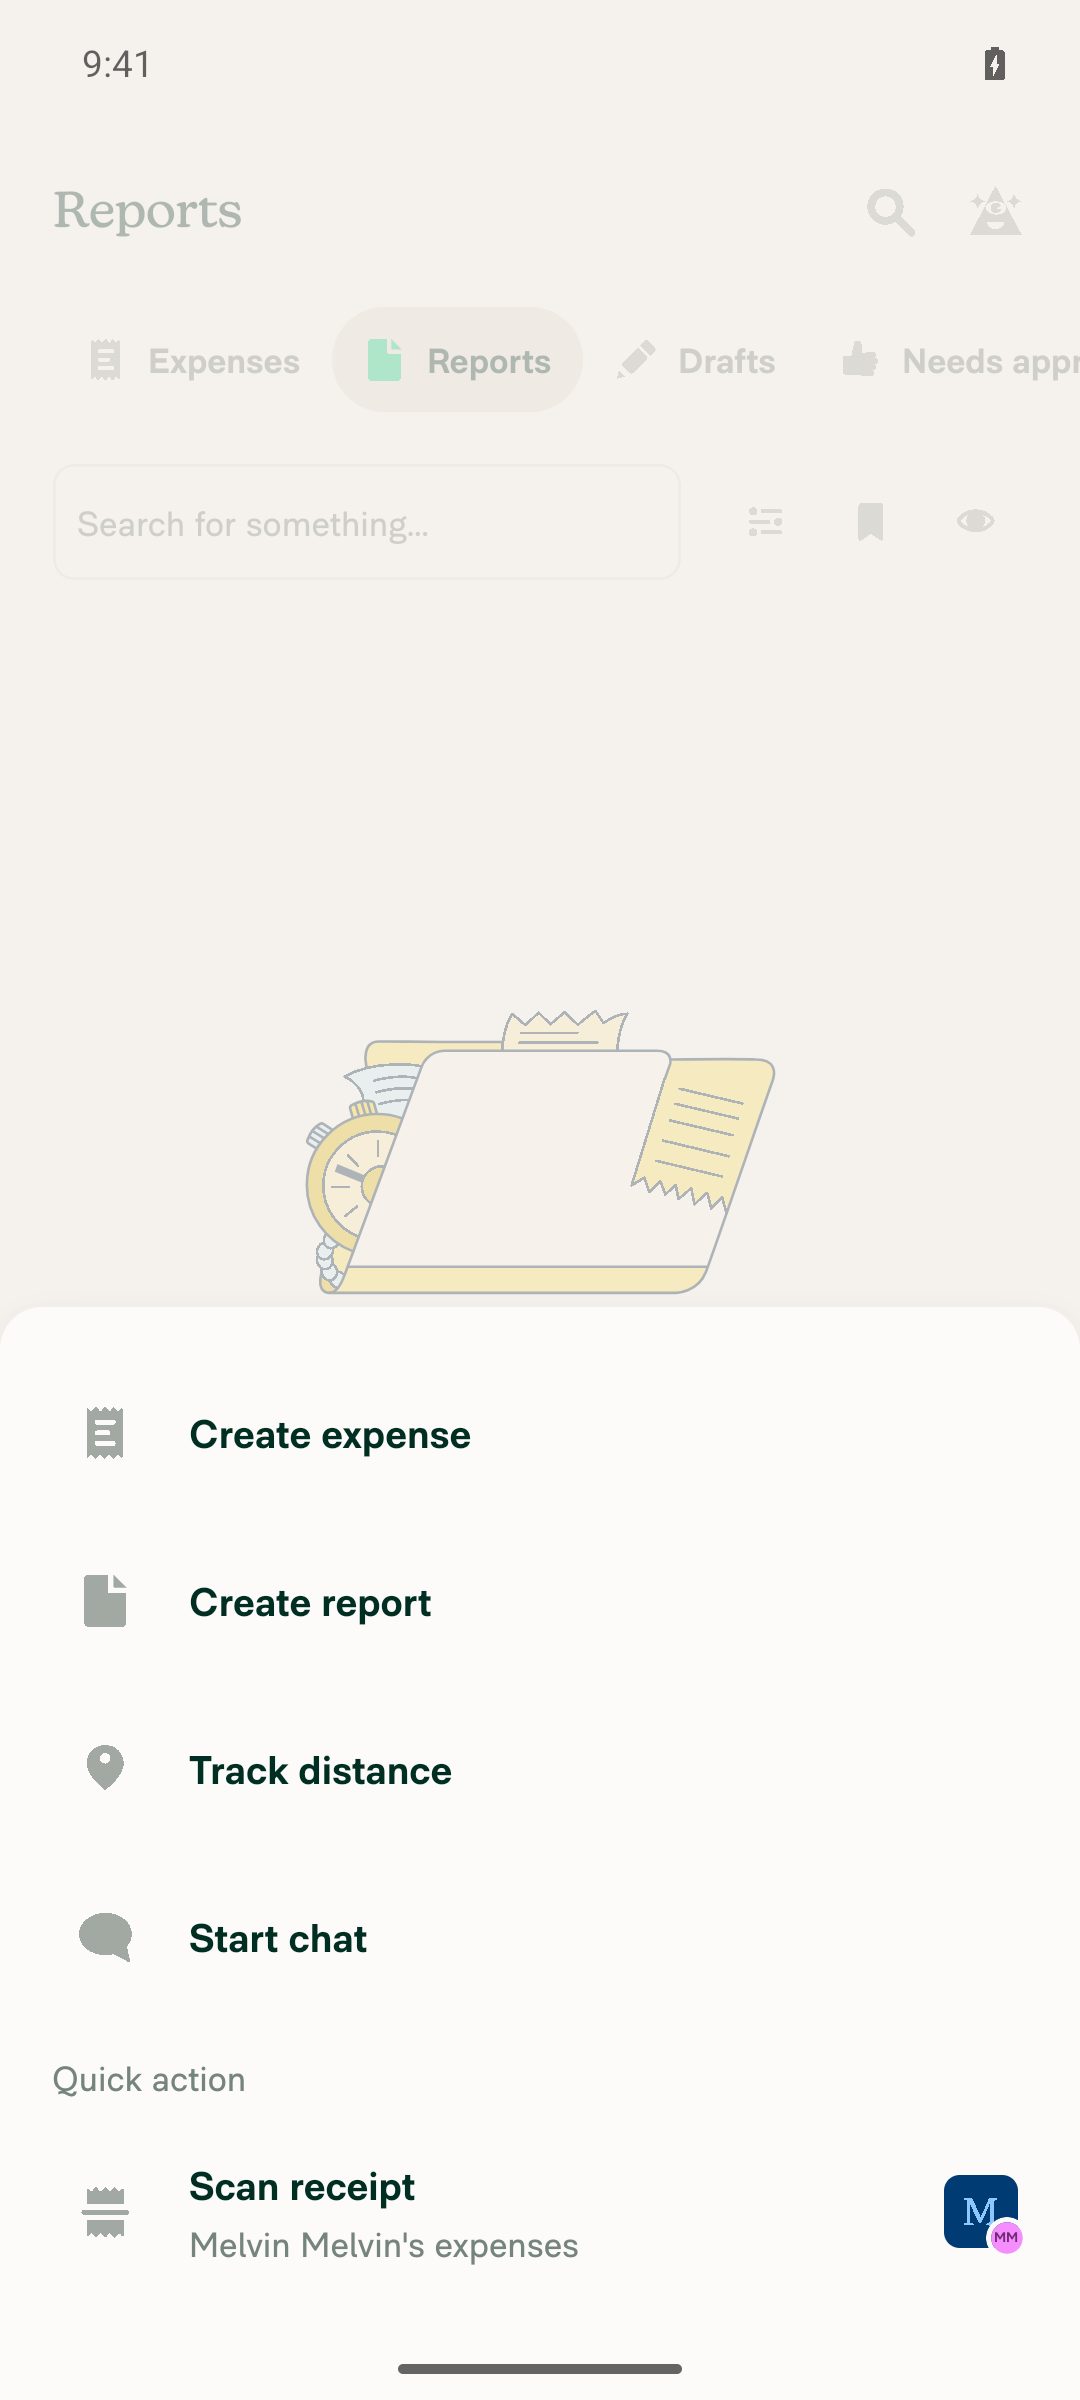
VERIFY 2: FAB > Create report opens the report creation flow, not the upgrade screenTapping the FAB opened the actions menu (Create expense, Create report, Track distance, Start chat, Scan receipt). Tapping "Create report" navigated straight to a new draft "Expense Report 2026-09-17" under the workspace with an "Add expense" CTA — no upgrade screen at any point.
FAB actions menu with Create report option
Draft report created after tapping Create report, no paywall
✅
VERIFY 3: Force-stop + relaunch, then hit Reports and the FAB during hydration — no paywall flashNot executed. Force-stopping and relaunching the app requires session lifecycle control this run does not own, so the cold-start hydration window — the case the new arePoliciesLoaded guard targets — is still unverified. This needs a manual QA pass or an automation run that owns app relaunch.
❌
VERIFY 4: No JS errors, red boxes, or console errors during the flows aboveReviewed the session app log covering workspace creation, Reports tab navigation, and the FAB > Create report flow. No fatal exceptions, crashes, red boxes, or JS exceptions. Only benign emulator warnings (missing camera, EGL format) and normal Onyx state logging.
✅

Two caveats worth noting: this ran on standalone Android NewDot, not HybridApp, and the account I tested with was a single-workspace Collect-trial member, so the EmptySearchView login fix (case 3 in the Explanation) wasn't exercised against a policy that carries the member's role only in employeeList. If you want that covered, point me at an account in that state.


view run · view recording

@MelvinBot

MelvinBot commented Sep 17, 2026 •

Copy link
Copy Markdown
Contributor Author

🤖 Web test steps verification results: ⚠️ partial

The reports empty state and the FAB create-report flow both show the correct non-paywall UI for a Collect-plan group workspace member. The hard-reload/cold-start race (VERIFY 3) could not be exercised, because a page reload during a driven web session risks dropping client auth into a magic-code wall this run cannot clear.

This PR still has no documented testing steps — the Tests and QA Steps sections are // TODO placeholders — so I derived the cases from the Explanation of Change, the same four I ran on Android. The account started mid-onboarding; completing onboarding auto-created a group workspace on the Collect plan, which is the account shape the bug affects.

Reports tab showing the created draft report in the list, no paywall

Step Status
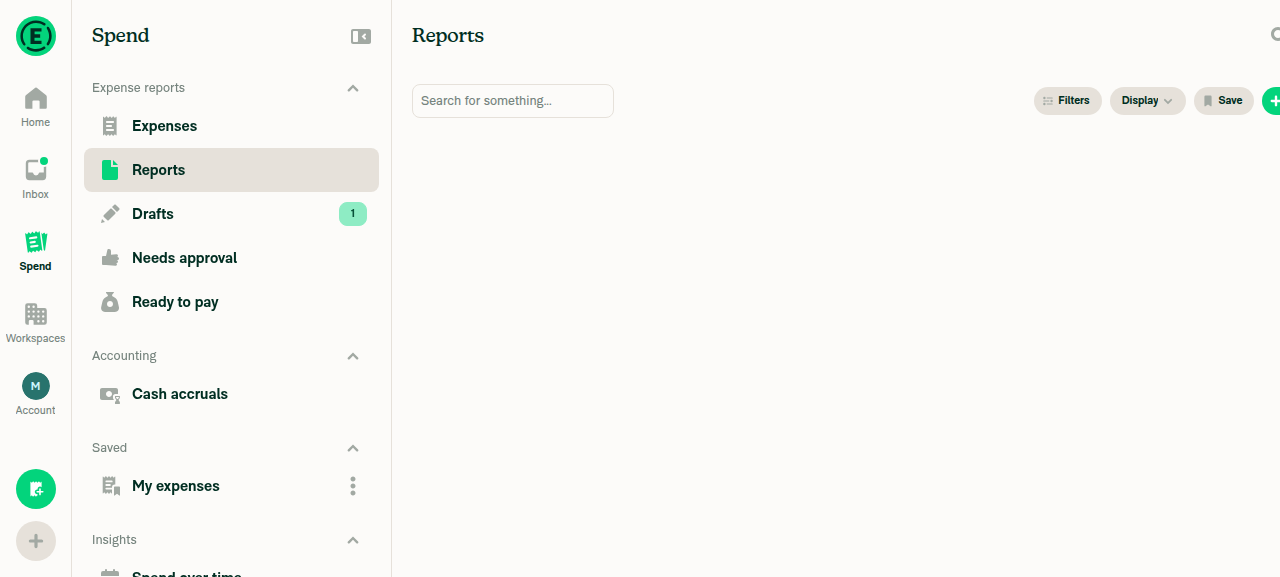
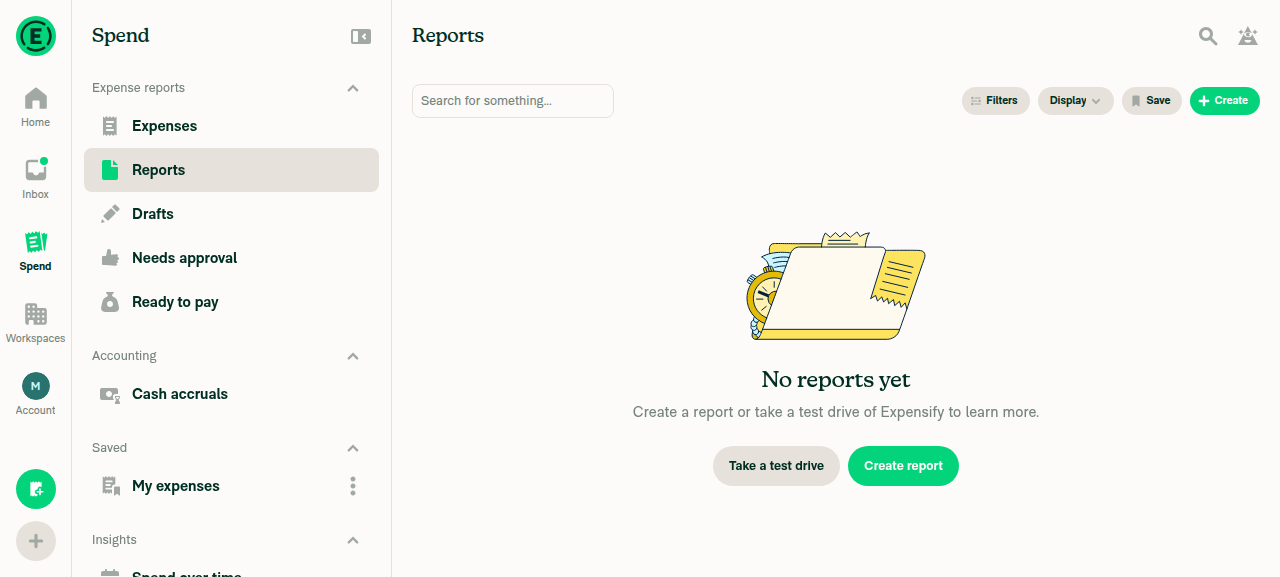
VERIFY 1: Reports tab does not show the Collect-plan upgrade screen; empty state is the normal reports empty stateSpend > Reports rendered heading "No reports yet" with "Create a report or take a test drive of Expensify to learn more", plus "Take a test drive" and "Create report" buttons — the standard empty state. A text search for "Reports are available on the Collect plan" returned no match.
Reports tab showing normal 'No reports yet' empty state, not the Collect plan upgrade screen
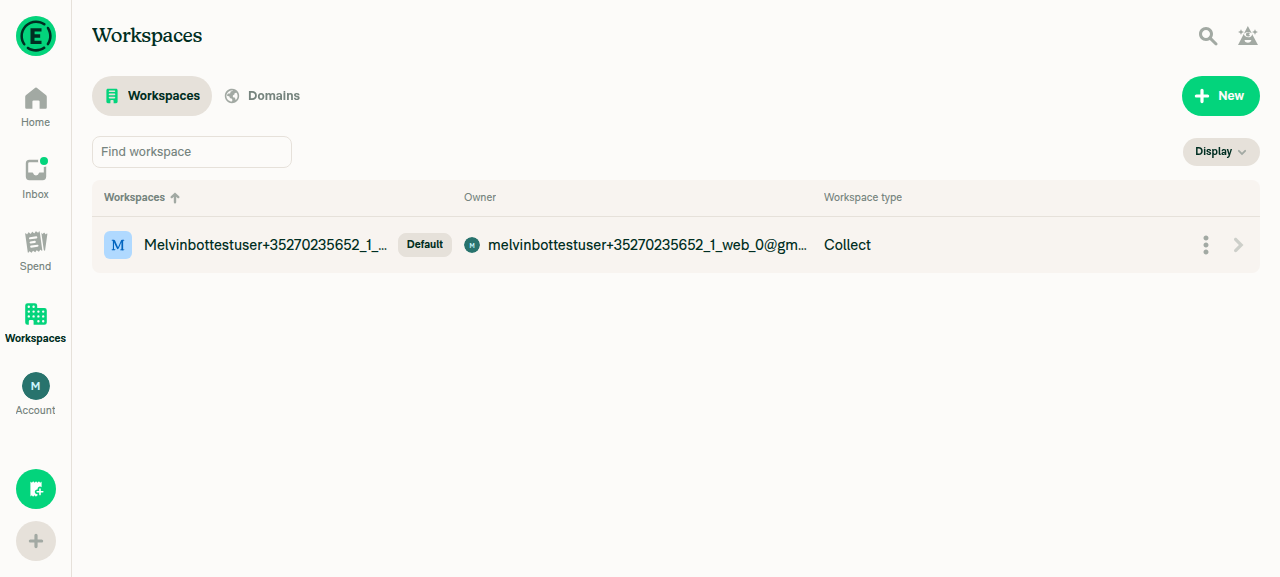
Settings > Workspaces confirming a Collect-plan group workspace exists
✅
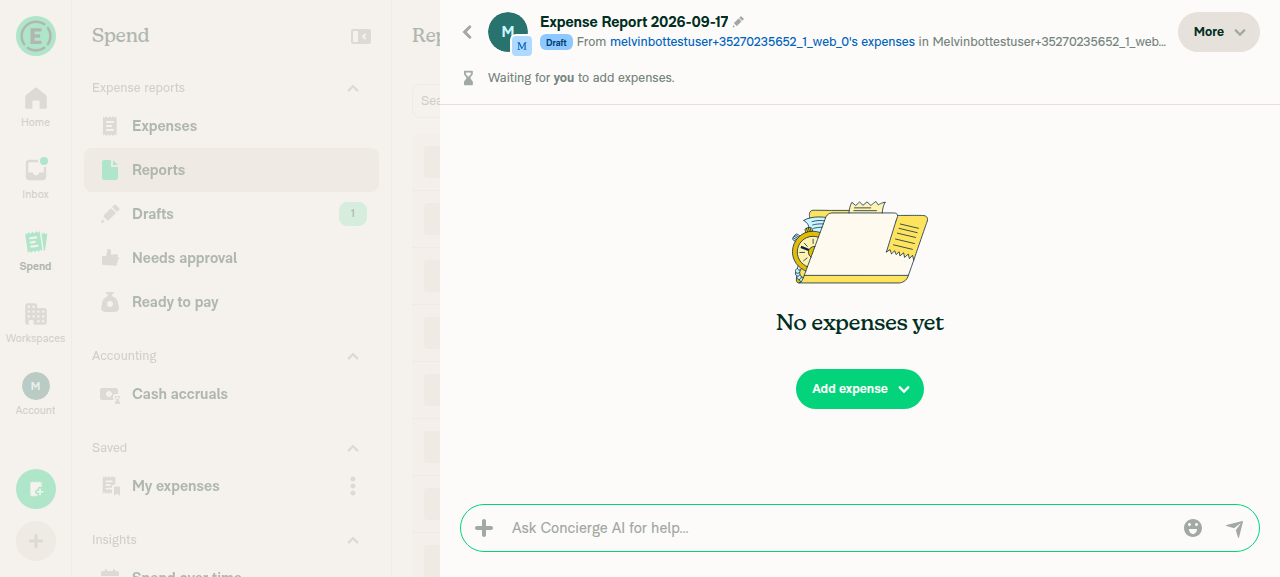
VERIFY 2: FAB > Create report opens report creation, not the Collect plan upgrade screenClicking the FAB opened a menu with Create expense, Create report, Track distance, Start chat, Scan receipt. Clicking "Create report" created a draft "Expense Report 2026-09-17" directly in the group workspace with a "No expenses yet" / "Add expense" state — no upgrade or paywall screen at any point.
FAB Create report opened a draft expense report, not the Collect plan upgrade screen
✅
VERIFY 3: Hard reload then immediate navigation to Reports/FAB shows no Collect-plan upgrade screen, even as a brief flash during hydrationNot exercised. Reloading during a driven web session drops client auth and can hit a magic-code wall this read-only run cannot clear, so the cold-start hydration window could not be safely triggered. This is the window the new arePoliciesLoaded guard specifically targets, so it remains the one unverified case — it needs manual QA or a dedicated e2e test that can tolerate a real page reload.
❌
VERIFY 4: No JS console errors during the above flowsThe web backend does not expose a browser-console log command, so this was verified by proxy rather than directly: every HTTP request captured during the flows (OpenSearchPage, Search, CreateAppReport, OpenReport, Ping, Log, SetNameValuePair) returned 200, and no error or "Something went wrong" text appeared in any accessibility snapshot or screenshot. Treat this as indicative, not conclusive.
⚠️

Same result shape as the Android run: the reachable flows are clean on both platforms, and the cold-start hydration race is unverified on both — blocked by app relaunch on Android and by page reload on Web. Since that race is the case the hydration guard exists to fix, it's worth covering with a unit test on the hook rather than through UI automation. Also note the EmptySearchView login fix (case 3 in the Explanation) wasn't exercised here either — this account's workspace was one where the role resolves without the employeeList fallback. Point me at an account whose role lives only in employeeList and I can cover that one.


view run · view recording

@MitchExpensify
MitchExpensify requested review from a team and removed request for a team September 18, 2026 03:25
@MitchExpensify
MitchExpensify marked this pull request as ready for review September 18, 2026 17:58
@MitchExpensify
MitchExpensify requested a review from a team as a code owner September 18, 2026 17:58
@melvin-bot
melvin-bot Bot requested review from huult and removed request for a team September 18, 2026 17:58
@melvin-bot

melvin-bot Bot commented Sep 18, 2026

Copy link
Copy Markdown

@huult Please copy/paste the Reviewer Checklist from here into a new comment on this PR and complete it. If you have the K2 extension, you can simply click: [this button]

@melvin-bot
melvin-bot Bot requested review from heyjennahay and removed request for a team September 18, 2026 17:59

@chatgpt-codex-connector chatgpt-codex-connector Bot left a comment

Copy link
Copy Markdown

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

💡 Codex Review

Here are some automated review suggestions for this pull request.

Reviewed commit: 57288aedff

ℹ️ About Codex in GitHub

Codex has been enabled to automatically review pull requests in this repo. Reviews are triggered when you

  • Open a pull request for review
  • Mark a draft as ready
  • Comment "@codex review".

If Codex has suggestions, it will comment; otherwise it will react with 👍.

When you sign up for Codex through ChatGPT, Codex can also answer questions or update the PR, like "@codex address that feedback".

// The active workspace can still be a valid destination even when the qualification pass came back
// empty, so check it before giving up. This has to run ahead of the upgrade path below, otherwise a
// perfectly valid active workspace can never rescue the user.
if (isPolicyValidForMovingExpenses(activePolicy, login, isPerDiemRequest, isTimeRequest)) {

Copy link
Copy Markdown

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

P1 Badge Validate roles from employeeList before upgrading

When a group policy stores the current member's role only in employeeList—the exact partially loaded shape handled by the EmptySearchView change—both the qualification pass and this new active-policy fallback call isPolicyValidForMovingExpenses, whose isPolicyMemberByRole check accepts only policy.role. The active workspace therefore still cannot rescue these members, and callers such as SearchActionsBarCreateButton route them to the reports upgrade screen even though its separate policy selector recognizes their workspace. Use the login-aware getPolicyRole fallback when validating policies.

Useful? React with 👍 / 👎.

Copy link
Copy Markdown
Contributor Author

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

Good catch — fixed in 0268312.

isPolicyMemberByRole now resolves the role through getPolicyRole(policy, login) instead of reading policy.role directly, so a workspace that only carries the member's role in employeeList is accepted here the same way getGroupPoliciesWhereReportCanBeCreated already accepts it via shouldShowPolicy. That removes the disagreement you described between this hook and SearchActionsBarCreateButton's own selector.

See src/hooks/usePolicyForMovingExpenses.ts:29.

Added a regression test for it — tests/unit/hooks/usePolicyForMovingExpenses.test.tsx — and confirmed it fails against the old policy.role-only check and passes with the fix.

Comment thread src/hooks/usePolicyForMovingExpenses.ts Outdated
return {policyForMovingExpensesID: activePolicyID, policyForMovingExpenses: activePolicy, shouldSelectPolicy: false, shouldNavigateToUpgradePath: false};
}

return {policyForMovingExpensesID: undefined, policyForMovingExpenses: undefined, shouldSelectPolicy: false, shouldNavigateToUpgradePath: arePoliciesLoaded};

Copy link
Copy Markdown

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

P2 Badge Block actions while the policy collection is loading

During the initial Onyx read, this returns the same false value used for a confirmed eligible policy, but the hook's consumers do not receive arePoliciesLoaded and therefore cannot distinguish the two states. For example, if a user clicks Create report in SearchTransactionsChangeReport during this window, its fall-through calls createNewReport and changeTransactionsReport with an undefined policy instead of waiting; this can optimistically create an unscoped report and move the selected transactions before policy hydration completes. Expose a loading state or otherwise make acting callers no-op until the collection is loaded.

Useful? React with 👍 / 👎.

Copy link
Copy Markdown
Contributor Author

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

You're right, and SearchTransactionsChangeReport is the one call site where the fall-through actually mutates. Fixed in 0268312.

The hook now returns arePoliciesLoaded, and createReport no-ops while the collection is loading rather than calling createNewReport/changeTransactionsReport with an undefined policy — the same guard useCreateReport uses.

I re-read the other shouldNavigateToUpgradePath consumers and left them alone deliberately: SearchActionsBarCreateButton, QuickCreationActionsBar, MoneyRequestView, and DynamicSplitExpenseEditPage all fall through to a workspace selector or report picker when no policy resolves, which is a state they already handle and which creates nothing. Only this one writes.

@huult

huult commented Sep 19, 2026

Copy link
Copy Markdown
Contributor

Tag me when it's ready

@MitchExpensify

Copy link
Copy Markdown
Contributor

@huult is this good to go?

@MitchExpensify

Copy link
Copy Markdown
Contributor

@MelvinBot what's the latest here? Can you make sure all comments are addressed and the PR is ready for review again?

MelvinBot and others added 2 commits September 22, 2026 20:20
…ydrationGuard

Co-authored-by: MitchExpensify <MitchExpensify@users.noreply.github.com>
…tating call site

- isPolicyMemberByRole now resolves the role via getPolicyRole, so a workspace
  that only carries the member's role in employeeList is accepted here the same
  way getGroupPoliciesWhereReportCanBeCreated already accepts it.
- Expose arePoliciesLoaded and no-op SearchTransactionsChangeReport's
  createReport while the policy collection loads, so it can never create a
  report with an undefined policy during the hydration window.
- Add unit tests for the hydration guard, the employeeList role fallback, and
  the managed card transaction path.

Co-authored-by: MitchExpensify <MitchExpensify@users.noreply.github.com>
@MelvinBot
MelvinBot requested a review from a team as a code owner September 22, 2026 20:34
@melvin-bot
melvin-bot Bot requested review from thesahindia and removed request for a team September 22, 2026 20:34
@melvin-bot

melvin-bot Bot commented Sep 22, 2026

Copy link
Copy Markdown

@thesahindia Please copy/paste the Reviewer Checklist from here into a new comment on this PR and complete it. If you have the K2 extension, you can simply click: [this button]

@MelvinBot

Copy link
Copy Markdown
Contributor Author

Both review comments are addressed and CI is green. One thing still blocks "ready for review", and it needs a person — see the bottom.

What I just pushed (0268312, plus a main merge):

  1. Codex P1 — role validation ignored employeeList. Real catch, and it undercut the PR's own fix. isPolicyMemberByRole read policy.role directly, which the backend only populates for the user's default workspace. It now resolves through getPolicyRole(policy, login), matching what getGroupPoliciesWhereReportCanBeCreated already does. Without it, the active-workspace fallback couldn't rescue exactly the members it was added for. Reply in thread.

  2. Codex P2 — callers couldn't tell "loading" from "eligible". Also correct, for one call site. The hook now returns arePoliciesLoaded, and SearchTransactionsChangeReport no-ops while the collection loads instead of creating a report with an undefined policy and moving transactions into it. I checked the other consumers and left them alone on purpose: they fall through to a workspace selector or report picker, which creates nothing. Reply in thread.

  3. Merged main. The branch was 1803 commits behind and the typecheck failure was stale drift in tests/unit/ModifiedExpenseMessageTest.ts — a file this PR never touched, already fixed on main. Clean merge, no conflicts. Typecheck now passes.

  4. Added unit tests — tests/unit/hooks/usePolicyForMovingExpenses.test.tsx. This covers the cold-start hydration race that neither the Android nor the Web run could exercise, since both were blocked on relaunching the app. I confirmed the employeeList test fails against the pre-fix code, so it's a real regression test.

CI: everything passes — typecheck, ESLint, Oxfmt, React Compiler, spellcheck, all 8 Jest shards, Bun tests, perf, builds. The only reds are Check independent approval and checklist, which clear when a reviewer signs off.

Still blocking: the Tests and QA Steps sections of the description are still // TODO placeholders, and the platform checkboxes and screenshots are unfilled. Those are the human co-author's to write — I won't fill in "I tested this on iOS Native" on someone else's behalf. Once someone adds those and the platform screenshots, huult can take it (they asked to be tagged when it's ready).

One caveat: I could not drive the app in a browser this run, so nothing here is newly verified in a live session. The claims above come from the code, the merged main diff, and the local + CI test runs.

@huult

huult commented Sep 22, 2026

Copy link
Copy Markdown
Contributor

@huult is this good to go?

@MitchExpensify Is this PR ready for review?

@huult

huult commented Oct 13, 2026

Copy link
Copy Markdown
Contributor

@thesahindia are you interested in reviewing? Since @huult is now technically the co-author, we need another C+ reviewer. And hopefully by then the unrelated Jest failure will be fixed and we'll just need to pull main here.

@thesahindia Do you have time to review this PR? If not, please let me know so I can ask another C+.

…ydrationGuard

Co-authored-by: huult <huult@users.noreply.github.com>
@MelvinBot

Copy link
Copy Markdown
Contributor Author

Synced with main. I merged the latest main into this branch in 8d6b3a5. The branch was 38 commits behind, and the merge had no conflicts. CI will now run against the updated branch.


view run

@thesahindia

Copy link
Copy Markdown
Member

@thesahindia are you interested in reviewing? Since @huult is now technically the co-author, we need another C+ reviewer. And hopefully by then the unrelated Jest failure will be fixed and we'll just need to pull main here.

@thesahindia Do you have time to review this PR? If not, please let me know so I can ask another C+.

On it. @huult, could you add the test steps?

@thesahindia

Copy link
Copy Markdown
Member

@MelvinBot, add these steps to the tests section

  1. Sign in to staging with a test account that belongs to one Collect or Control workspace.

  2. Open the workspace's Members page to load its member list.

  3. Open Search → Reports and let it finish loading.

  4. In Chrome DevTools → Network, select Offline.

  5. In the console, run:

    const login = (await Onyx.get('session')).email;
    const policies = await Onyx.get('policy_');
    
    const [key, policy] = Object.entries(policies).find(
        ([, p]) => ['team', 'corporate'].includes(p?.type)
    );
    
    if (!policy.employeeList?.[login]?.role) {
        throw new Error('Open the workspace Members page to load your membership first.');
    }
    
    window.reportReproBackup = {key, policy: structuredClone(policy)};
    
    const {role, ...partialPolicy} = policy;
    await Onyx.set(key, partialPolicy);
  6. Without reloading, select Create → Create report in the Search header.

  7. Verify the result:

    • Before the fix: the Collect upgrade screen appears despite the account's workspace membership.
    • With the fix: the app recognizes the membership and continues through the normal report flow.
  8. Before reloading or going online, restore the original data:

    await Onyx.set(
        window.reportReproBackup.key,
        window.reportReproBackup.policy
    );
    delete window.reportReproBackup;
  9. In DevTools → Network, select No throttling.

@thesahindia

thesahindia commented Oct 14, 2026 •

Copy link
Copy Markdown
Member

Reviewer Checklist

  • I have verified the author checklist is complete (all boxes are checked off).
  • I verified the correct issue is linked in the ### Fixed Issues section above
  • I verified testing steps are clear and they cover the changes made in this PR
    • I verified the steps for local testing are in the Tests section
    • I verified the steps for Staging and/or Production testing are in the QA steps section
    • I verified the steps cover any possible failure scenarios (i.e. verify an input displays the correct error message if the entered data is not correct)
    • I turned off my network connection and tested it while offline to ensure it matches the expected behavior (i.e. verify the default avatar icon is displayed if app is offline)
  • I checked that screenshots or videos are included for tests on all platforms
  • I included screenshots or videos for tests on all platforms
  • I verified that the composer does not automatically focus or open the keyboard on mobile unless explicitly intended. This includes checking that returning the app from the background does not unexpectedly open the keyboard.
  • I verified tests pass on all platforms & I tested again on:
    • Android: HybridApp
    • Android: mWeb Chrome
    • iOS: HybridApp
    • iOS: mWeb Safari
    • MacOS: Chrome / Safari
  • If there are any errors in the console that are unrelated to this PR, I either fixed them (preferred) or linked to where I reported them in Slack
  • I verified any copy / text that was added to the app is either coming verbatim from figma or has been approved by marketing (in order to get marketing approval, ask the Bug Zero team member to add the Waiting for copy label to the issue)
  • If a new code pattern is added I verified it was agreed to be used by multiple Expensify engineers
  • I verified other components that can be impacted by these changes have been tested, and I retested again (i.e. if the PR modifies a shared library or component like Avatar, I verified the components using Avatar have been tested & I retested again)
  • If a new component is created I verified that:
    • A similar component doesn't exist in the codebase
    • All props are defined accurately
    • The component has a clear name that is non-ambiguous and the purpose of the component can be inferred from the name alone
    • The only data being stored in the state is data necessary for rendering and nothing else
    • The component has the minimum amount of code necessary for its purpose, and it is broken down into smaller components in order to separate concerns and functions
  • If the PR modifies code that runs when editing or sending messages, I tested and verified there is no unexpected behavior for all supported markdown - URLs, single line code, code blocks, quotes, headings, bold, strikethrough, and italic.
  • If the PR modifies a generic component, I tested and verified that those changes do not break usages of that component in the rest of the App (i.e. if a shared library or component like Avatar is modified, I verified that Avatar is working as expected in all cases)
  • If the PR modifies a component related to any of the existing Storybook stories, I tested and verified all stories for that component are still working as expected.
  • If the PR modifies a component or page that can be accessed by a direct deeplink, I verified that the code functions as expected when the deeplink is used - from a logged in and logged out account.
  • If the PR modifies the UI (e.g. new buttons, new UI components, changing the padding/spacing/sizing, moving components, etc) or modifies the form input styles:
    • I verified that all the inputs inside a form are aligned with each other.
    • I added Design label and/or tagged @Expensify/design so the design team can review the changes.
  • If the PR adds or modifies the UI:
    • I asked an AI agent to review the changes for accessibility issues and addressed its findings.
    • I tested with a screen reader (VoiceOver on macOS) and verified all new/changed elements are reachable with a logical focus order.
    • I verified all new/changed elements have meaningful accessible names and roles.
    • I verified state changes are announced (e.g. checked/unchecked, expanded/collapsed, selected).
  • For any bug fix or new feature in this PR, I verified that sufficient unit tests are included to prevent regressions in this flow.
  • If the main branch was merged into this PR after a review, I tested again and verified the outcome was still expected according to the Test steps.
  • I have checked off every checkbox in the PR reviewer checklist, including those that don't apply to this PR.

Screenshots/Videos

Android: HybridApp
Screen.Recording.2026-10-14.at.7.30.35.AM.mov
Android: mWeb Chrome
Screen.Recording.2026-10-14.at.6.47.45.AM.mov
iOS: HybridApp
Screen.Recording.2026-10-14.at.7.21.16.AM.mov
iOS: mWeb Safari
Screen.Recording.2026-10-14.at.7.06.28.AM.mov
MacOS: Chrome / Safari
Screen.Recording.2026-10-14.at.6.30.36.AM.mov

@MelvinBot

Copy link
Copy Markdown
Contributor Author

Added all 9 steps to the Tests section of the PR description, in place of the TODO placeholder. I kept the "Verify that no errors appear in the JS console" checkbox below them and left the rest of the description unchanged.


view run

@huult

huult commented Oct 14, 2026

Copy link
Copy Markdown
Contributor

@MelvinBot Please add [No QA] to the PR title.

@MelvinBot MelvinBot changed the title [Payment due @huult] Stop routing group workspace members to the reports upgrade screen [No QA] [Payment due @huult] Stop routing group workspace members to the reports upgrade screen Oct 14, 2026
@MelvinBot

Copy link
Copy Markdown
Contributor Author

I added [No QA] to the PR title. The new title is:

[No QA] [Payment due @huult] Stop routing group workspace members to the reports upgrade screen

I kept the existing [Payment due @huult] tag.


view run

@github-actions

Copy link
Copy Markdown
Contributor

🚧 francoisl has triggered a test Expensify/App build. You can view the workflow run here.

@github-actions

This comment has been minimized.

@francoisl
francoisl merged commit 7237dcf into main Oct 14, 2026
45 of 47 checks passed
@francoisl
francoisl deleted the claude-reportUpgradeHydrationGuard branch October 14, 2026 22:42
@github-actions

Copy link
Copy Markdown
Contributor

🚧 francoisl has triggered a test Expensify/App build. You can view the workflow run here.

@francoisl francoisl mentioned this pull request Oct 14, 2026
38 tasks done
@OSBotify

Copy link
Copy Markdown
Contributor

🚀 Deployed to staging by https://github.com/francoisl in version: 9.5.10-0 🚀

platform result
🕸 web 🕸 success ✅
🤖 android 🤖 success ✅
🍎 iOS 🍎 success ✅

@MelvinBot

Copy link
Copy Markdown
Contributor Author

No help site update is needed. This bug fix stops sending group workspace members to the Collect plan upgrade screen, so the app now does what members already expect, and no article describes that upgrade screen.


view run

@OSBotify

Copy link
Copy Markdown
Contributor

🚀 Deployed to staging by https://github.com/francoisl in version: 9.5.12-0 🚀

platform result
🕸 web 🕸 success ✅
🤖 android 🤖 success ✅
🍎 iOS 🍎 success ✅

@MelvinBot

Copy link
Copy Markdown
Contributor Author

No help site update is needed. This bug fix stops sending group workspace members to the Collect plan upgrade screen, so the app now does what members already expect, and no article describes that upgrade screen. My earlier review still applies, because the PR's changes have not changed since then.


view run

@OSBotify

Copy link
Copy Markdown
Contributor

🚀 Deployed to production by https://github.com/cristipaval in version: 9.5.12-1 🚀

platform result
🕸 web 🕸 success ✅
🤖 android 🤖 success ✅
🍎 iOS 🍎 success ✅

Bundle Size Analysis (Sentry):

@melvin-bot

melvin-bot Bot commented Oct 16, 2026

Copy link
Copy Markdown

🤖 Payment issue created: #104214

Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

Melvin-Test-Android Melvin-Test-Web Triggers Melvin to run the testing steps of the PR on web Ready To Build

Projects

None yet

Development

Successfully merging this pull request may close these issues.

6 participants