Repository navigation
feat: add Go framework support - #945
Conversation


🧙 Wizard CIRun the Wizard CI and test your changes against wizard-workbench example apps by replying with a GitHub comment using one of the following commands: Test all apps:
Test all apps in a directory:
Test an individual app:
Show more apps
Results will be posted here when complete. |

6e5076c to
57700c0
Compare

Adds Go as a supported framework following the backend-framework pattern (Rails):

- Integration.go enum entry at the end of the frameworks block, before the language fallbacks
- GO_AGENT_CONFIG in src/frameworks/go/ — claims a go.mod with a module directive, gathers the go directive version as agent context, installs via go get github.com/posthog/posthog-go
- goModulesPackageManager helper + FRAMEWORK_REGISTRY entry
- bash-fence grammar for the go binary: get/build/vet/fmt/version/list plus go mod tidy/download/verify/graph/why; run/test/generate stay denied (arbitrary code execution), go mod edit stays denied (rewrites module requirements)
- Pins framework: go on integration-go in the variant-resolution contract test, matching context-mill PR #267 which must release before this merges
- Marks go.mod as a real framework target in the agentic manifest comment

Generated-By: PostHog Code
Task-Id: 9c949855-7611-48f2-b8b5-7aa4112543e5
57700c0 to
5b9202e
Compare

go build/vet were allowed by subcommand without inspecting flags, so
`go build -toolexec=/tmp/x.sh` would run an arbitrary program on every
build. Deny the -toolexec flag explicitly (both = and space forms) and
add attack-corpus tests.

Co-Authored-By: Claude Opus 4.8 <noreply@anthropic.com>

Additive conflicts against the Flutter work: both language helpers kept in
bash-fence, package-manager, and their tests.

Co-Authored-By: Claude Opus 5 <noreply@anthropic.com>

| // allowed verbs above are not safe with it. Deny it explicitly. | ||
| const toolexec = parts | ||
| .slice(2) | ||
| .find((p) => p === '-toolexec' || p.startsWith('-toolexec=')); |

There was a problem hiding this comment.
Critical: Arbitrary program execution through Go tool flags
A malicious repository can include an executable payload and prompt the agent to run go vet -vettool=./payload ./...; this passes the fence and causes Go to execute the payload. The current check also misses --toolexec, so block both spellings of both execution flags.
| .find((p) => p === '-toolexec' || p.startsWith('-toolexec=')); | |
| .find((p) => /^--?(?:toolexec|vettool)(?:=|$)/.test(p)); |

PR overviewThis pull request adds Go framework support, including updates to the Bash command fence for Go build and analysis commands. Two security issues remain open, and none have yet been addressed. A malicious repository can use permitted Go tool flags to execute an arbitrary program, while unrestricted build output paths can place executable Git hooks that run later. The direct program-execution path makes the current security posture high risk. Open issues (2)
Fixed/addressed: 0 · PR risk: 8/10 |

|
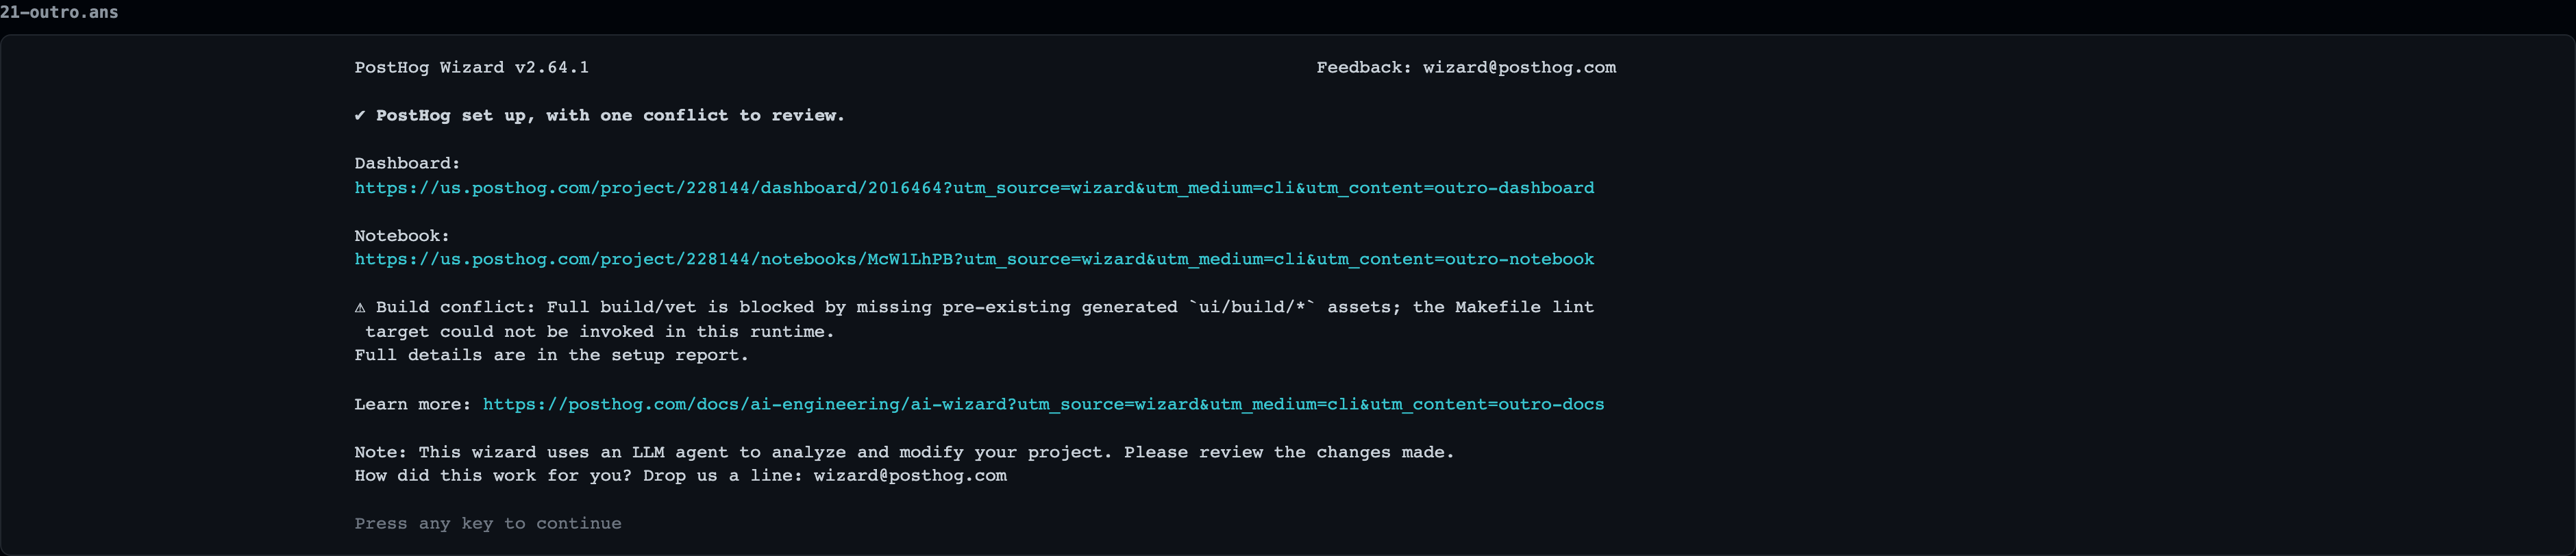
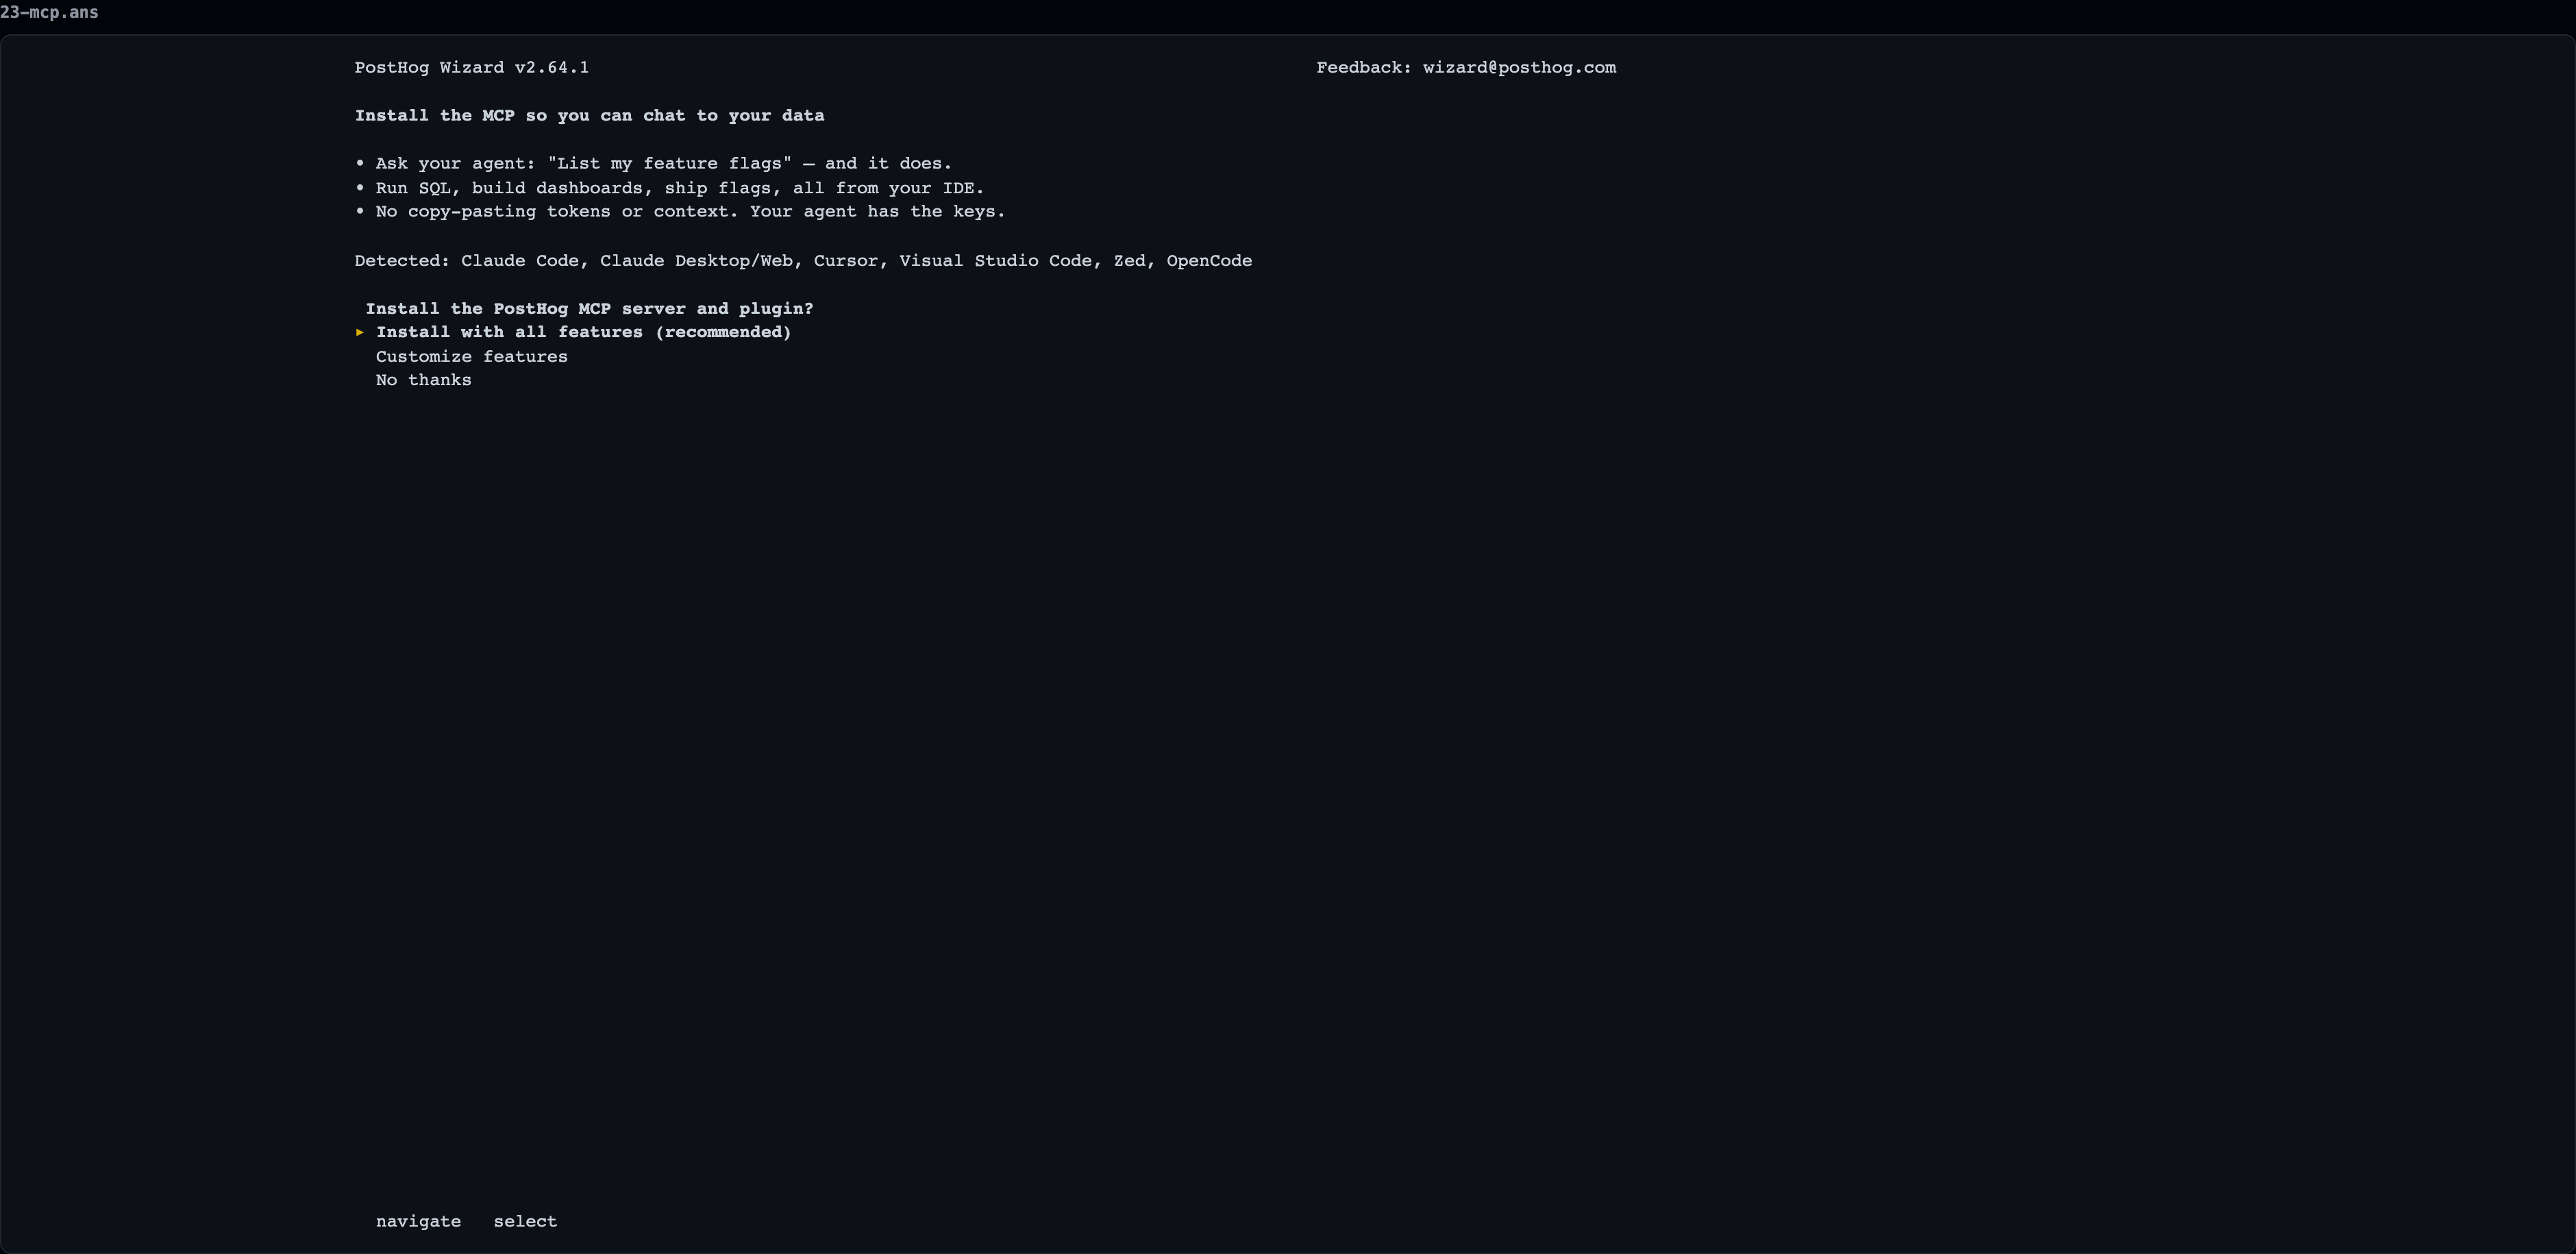
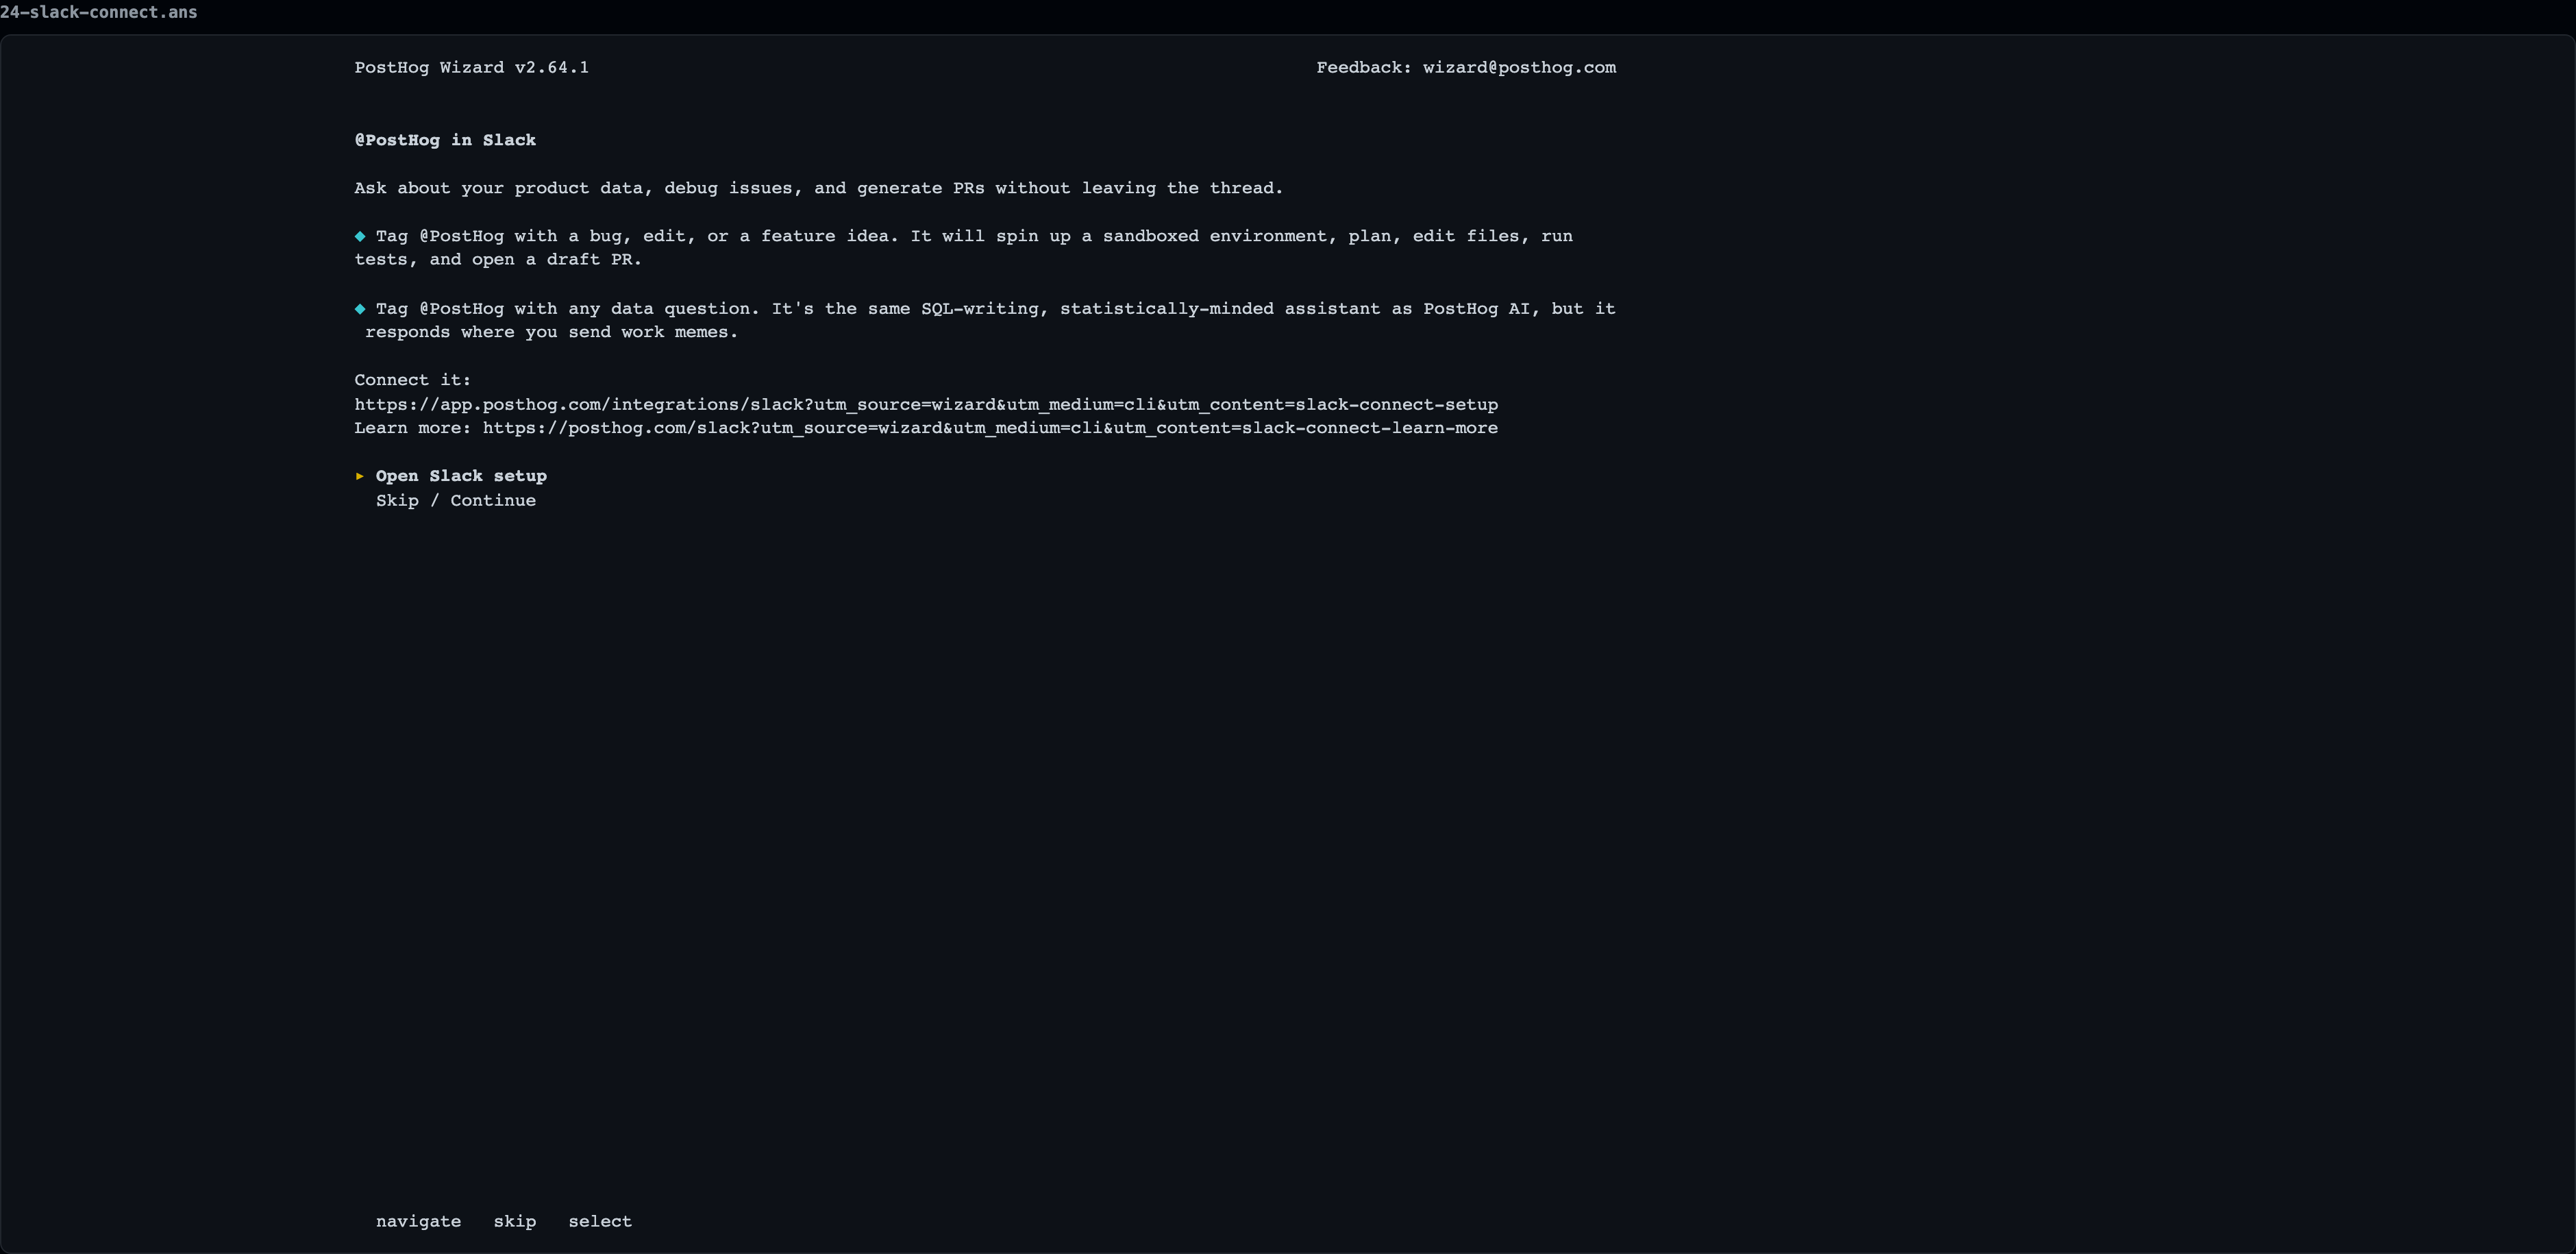
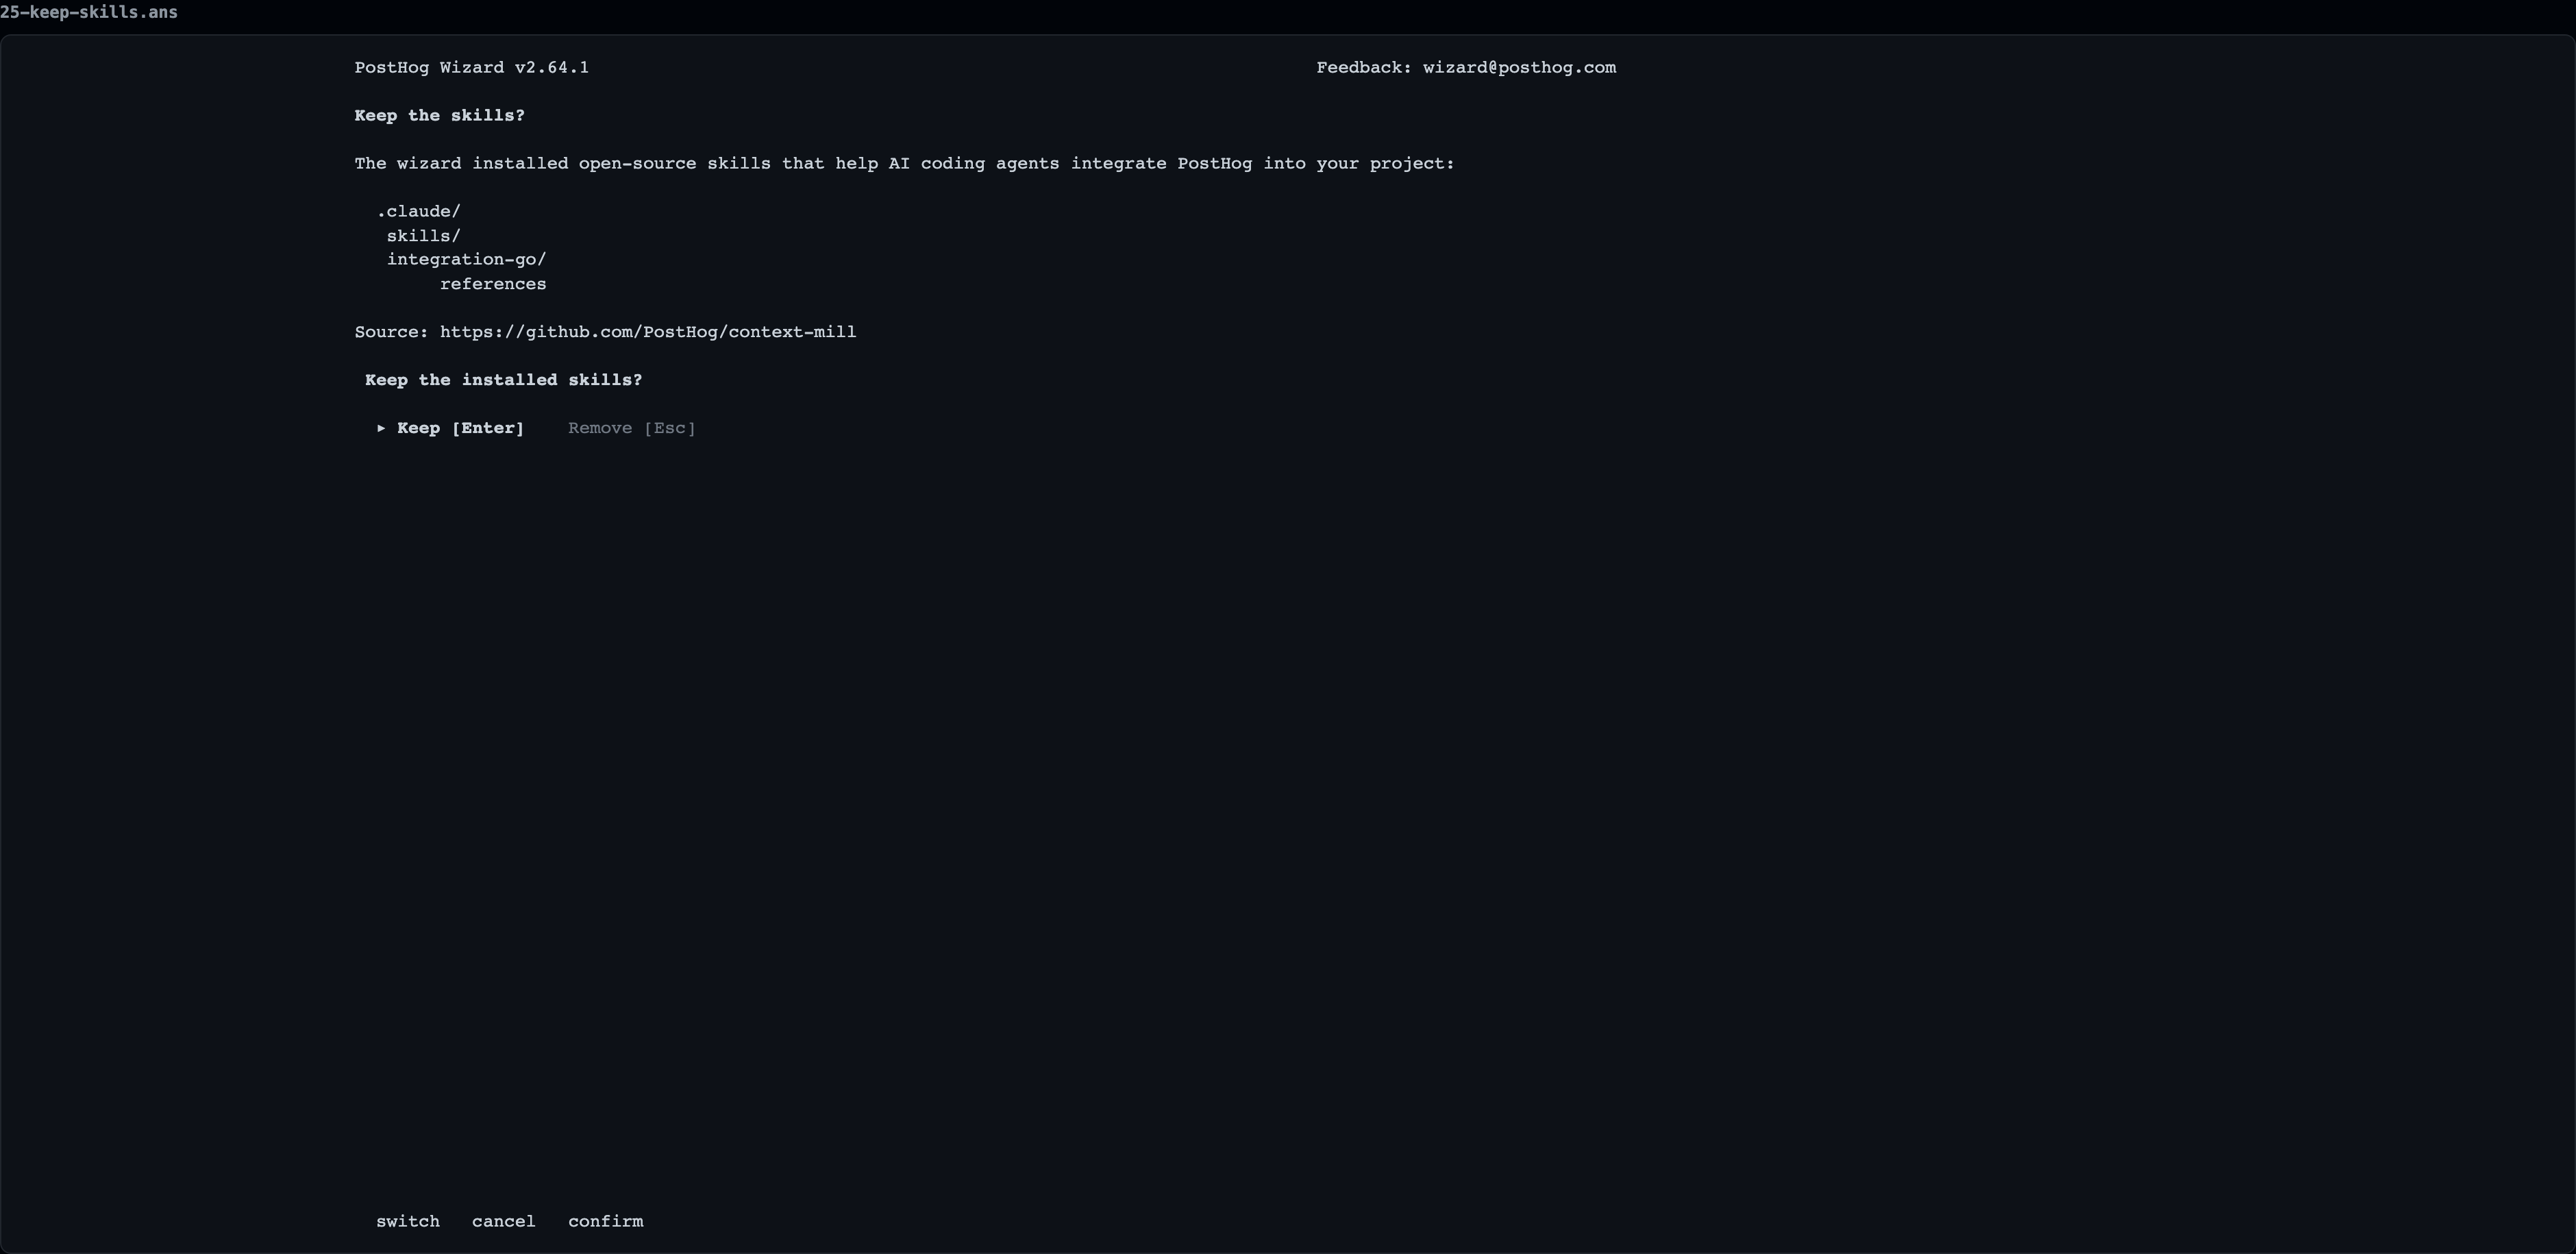
Full e2e run of this PR pair (wizard #945 + context-mill #267, both with main merged in) against gotify/server — real Go server, Outcome: PostHog set up — dashboard and notebook created through prod MCP, Note: the branch as filed fails at the dashboard step — its agent prompts predate the All 25 TUI frames
|

The result JSON parsed package.json and pubspec.yaml only, so Go, Rust, Java,
and Elixir runs reported hasPosthogDep false; a *.env file like gotify's also
failed the .env prefix check.

Co-Authored-By: Claude Opus 5 <noreply@anthropic.com>
…sitive

Co-Authored-By: Claude Opus 5 <noreply@anthropic.com>
| // go's verb list is closed: dependency + verify commands only. run/test/generate | ||
| // execute project-defined code; `go mod edit` can rewrite module requirements | ||
| // to arbitrary sources, so only the read/refresh mod subcommands are allowed. | ||
| const GO_SUBCOMMANDS = ['get', 'build', 'vet', 'fmt', 'version', 'list']; |
There was a problem hiding this comment.
Medium: Build output can install executable Git hooks
Allowing go build with unrestricted flags admits commands such as go build -o .git/hooks/pre-commit ./cmd/payload. An attacker-controlled repository can use this to install its payload as an executable hook that runs during a later commit; reject -o or validate that its destination cannot target .git or other executable control paths.


Related PRs:
mainand can merge on its own, in any order relative to the sibling Go/Elixir/Rust/Java framework PRs.Adds Go as a supported framework, following the backend-framework pattern (Rails):
Integration.goenum entry at the end of the frameworks block, before the language fallbacks — a Go repo with an embedded frontendpackage.jsonstill resolves to Go (covered by a new detection test)GO_AGENT_CONFIGinsrc/frameworks/go/— claims ago.modwith amoduledirective (a bare directory of.gofiles falls through); gathers thego 1.xdirective as agent context; installs viago get github.com/posthog/posthog-gogoModulesPackageManagerhelper +FRAMEWORK_REGISTRYentrygo: allowsget|build|vet|fmt|version|listandgo mod tidy/download/verify/graph/why;go run/test/generatestay denied (arbitrary code execution) andgo mod editstays denied (can rewrite module requirements to arbitrary sources)framework: goonintegration-goin the variant-resolution contract test, matching the context-mill PR aboveWhy: the wizard docs page lists Go as "Coming soon"; instead of removing the label (posthog.com#18797), we're making the wizard actually support it.
Verification:
pnpm build✅,pnpm test✅ (1536 tests, incl. new go detect + fence tests),pnpm fix✅Created with PostHog Code