Repository navigation
[Bug]: New Codex runtime entries can disable existing shadow-home providers #5817
Description

Summary
T3's Codex shadow-home setup only links entries that already exist in the shared home when materialization runs. If a later Codex update creates a new top-level runtime entry in both the shared and shadow homes, the next materialization rejects the shadow copy and disables the provider.
Codex 0.147 introduced queue_1.sqlite, which triggers this today. The same failure can recur when Codex adds another home entry.
Reproduction
- Configure the documented multi-account layout: one shared
homePathand another account using thathomePathplus a separateshadowHomePath. - Start with no
queue_1.sqlitein either home and let T3 materialize the shadow home. - Run Codex 0.147 against both effective homes. Codex creates a regular queue database in each.
- Refresh provider status or restart T3.
The shadow-home provider becomes disabled:
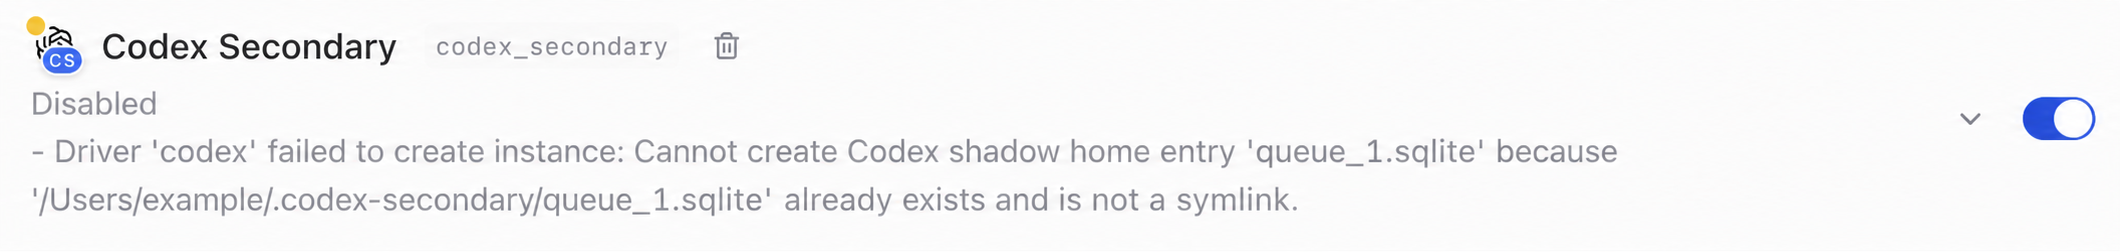
Driver 'codex' failed to create instance: Cannot create Codex shadow home entry 'queue_1.sqlite' because '<shadow-home>/queue_1.sqlite' already exists and is not a symlink.
A minimal unit repro is to create regular sharedHome/queue_1.sqlite and shadowHome/queue_1.sqlite files, then call materializeCodexShadowHome(layout).
Why it happens
T3 lists the current shared-home entries, then ensureSymlink rejects any existing regular shadow entry. There is no recovery path; the conflict becomes a provider creation error.
Codex added the queue DB in openai/codex@b87981a. In the affected installation, the shared DB and two shadow DBs were automatically created within six seconds, confirming this was runtime-created state rather than a copied home.
Expected behavior
Codex upgrades that add runtime entries should not disable existing shadow-home providers. T3 should reconcile ownership safely or offer a targeted recovery path without silently deleting user data.
Acceptance criteria
- New Codex home entries created after an earlier materialization do not leave providers disabled.
- The solution is resilient to future filenames rather than only adding
queue_1.sqliteto an allowlist. - Existing data is preserved; SQLite families such as the base DB, WAL, and SHM are handled together.
- Tests cover creation between materialization passes and an existing regular shadow entry.
Environment
- T3
mainat1a003e383ac6b10258b8100c2617d938c4f06c69 - Codex CLI 0.147.0
- macOS 26.5.2, Apple Silicon
Workaround
With related processes stopped, backing up and removing the shadow queue_1.sqlite, queue_1.sqlite-wal, and queue_1.sqlite-shm files allows T3 to create the shared link. This is manual, potentially data-destructive, and does not address future Codex entries.
Activity
[-][Bug]: Codex 0.147 queue DB disables shadow-home provider instances[/-][+][Bug]: New Codex runtime entries can disable existing shadow-home providers[/+]EwenGG commentedon Aug 20, 2026
I can confirm this issue on Windows, with an additional sidecar-only variant that may be relevant to the proposed fix in #7201.
Environment
0.0.34-nightly.20260820.11410.148.010.0.26200, x64Sanitized configuration:
{
  "driver": "codex",
  "enabled": true,
  "config": {
    "homePath": "C:\\Users\\<user>\\.codex",
    "shadowHomePath": "C:\\Users\\<user>\\.codex_p"
  }
}
Observed behavior
This has recurred across several recent T3 Code Nightly and Codex updates.
On startup or provider refresh, the secondary Codex provider is disabled during
materializeCodexShadowHome. T3 encounters a regular SQLite runtime sidecar in the shadow home where it expects a symbolic link, then aborts provider creation.Exact error
The corresponding server trace reports:
Previous occurrences on the same machine failed on other members of the same class of runtime files:
Because materialization stops at the first conflict, the filename displayed by T3 does not represent the complete set of conflicting entries.
Shadow-home state at failure time
A complete inspection of the shadow-home root found eight regular SQLite sidecar files:
logs_2.sqlite-shmlogs_2.sqlite-walmemories_1.sqlite-shmmemories_1.sqlite-walqueue_1.sqlite-shmqueue_1.sqlite-walstate_5.sqlite-shmstate_5.sqlite-walThe problem was therefore not limited to
queue_1.sqlite.Importantly, the corresponding base database entries were still symbolic links to the shared Codex home:
In this occurrence, the divergence was specifically:
This is slightly different from the original #5817 reproduction, where the shadow base database itself is described as becoming a regular file.
Recurrence evidence
Retained local logs show repeated failures on at least two consecutive days:
memories_1.sqlite-shmlogs_2.sqlite-shmqueue_1.sqliteThe problem has returned after multiple manual recoveries and subsequent updates or restarts. It is not an isolated stale file left by a single interrupted process.
Different SQLite families become affected at different times. Some sidecars already existed from the previous day, while others were created or rewritten during the next T3/Codex run.
Impact
Recovery confirmation
For diagnostic purposes, I backed up and moved all eight regular
*.sqlite-waland*.sqlite-shmfiles out of the shadow home. I did not modify the privateauth.jsonormodels_cache.jsonfiles.I then disabled and re-enabled only the affected provider instance.
After rematerialization:
This immediately restored the provider, confirming that the regular SQLite sidecars directly caused provider creation to fail.
However, the same class of conflict has returned after later updates or runs, so this procedure is only a temporary recovery.
Relation to PR #7201
PR #7201 appears to target the same underlying class of failure:
#7201
Its stated goal—keeping newly created Codex SQLite state shadow-local and treating a base database plus its WAL/SHM sidecars as one family—matches the recurring behavior observed here.
However, my captured state includes a sidecar-only divergence: the shadow base
.sqliteentry remained a symbolic link while its-waland-shmentries were regular files.The PR description and diff appear to select shadow-local ownership when the shadow base database is already a regular file. I cannot confirm whether it also covers the observed case where only the WAL/SHM members have become regular files.
This Windows reproduction may therefore be useful for validating #7201 against both forms:
I am not proposing a separate implementation here. I am documenting the additional observed state so that the existing fix can be evaluated against the complete failure mode.
tgangso commentedon Oct 7, 2026
Adding updated Windows findings here as requested when #17005 was closed as a duplicate.
Environment
0.0.46-nightly.20261007.27870.161.0Observed failure
Three Codex providers failed to initialize with this sanitized error:
Inspection confirmed the sidecar-only state already described in this issue: base SQLite databases were symlinks to the shared home, while some
-shmand-walfiles were regular files in the shadow homes. Some WAL files were nonempty.In the installed build,
materializeCodexShadowHomeattempts to link shared-home entries, andensureSymlinkrejects these existing regular files. The initial creation of the conflicting files was not captured; no fresh-install reproduction or repository regression test was run.Workaround and verification
The conflicting files were backed up and moved out of the shadow homes, allowing T3 to recreate the links. Each affected provider's launch arguments were also configured to set
sqlite_homeexplicitly to the shared Codex directory.After T3 reloaded the settings, all three provider connection probes succeeded. No regular SQLite sidecar conflicts remained at that check. Long-term recurrence has not yet been tested.
This confirms the failure on the versions above and records the observed recovery. It is not a recommendation to delete SQLite sidecars or a claim that a permanent upstream fix has been verified. Related shared-directory approach: #9229.
dustenhubbard commentedon Oct 8, 2026
Another entry for this issue, from Codex 0.161.0:
cloud-config-bundle-cache.json. This one should not be linked, either.Environment
0.0.46-nightly.20261007.2774(desktop)0.161.0~/.codex, and a second instance withshadowHomePathset to~/.codex-t3/workWhat happened
After a T3 restart, the second instance showed only "Disabled" in Settings → Providers, with its toggle still on. Its status cache had stopped updating at the restart. The settings were unchanged.
cloud-config-bundle-cache.jsonexisted as a regular file in both the shared home and the shadow home. In the installed build,PRIVATE_ENTRY_NAMESisauth.jsonandmodels_cache.json, somaterializeCodexShadowHometries to link this file andensureSymlinkrejects the regular copy. I did not find the error text in the server trace. I am going by the file state and the code.Why linking is the wrong fix for this file
The file is per-account. It holds
chatgpt_user_id,account_id, and the workspace's signed enterpriseconfig_tomlandrequirements_toml, with a one-hour expiry. If it were shared, one account could pick up another account's workspace policy. It belongs withauth.jsonandmodels_cache.json.Linking also does not last. I deleted the shadow copy and turned the provider off and on. The provider came back, but within seconds there was a regular file in the shadow home again, and the shared copy had not changed. So the next restart would disable the provider again.
Workaround
A small job deletes the shadow copy every two minutes, so a restart does not find one. Codex fetches the bundle again when it needs it. This only matters until the file is treated as private.
Suggested fix
Add
cloud-config-bundle-cache.jsontoPRIVATE_ENTRY_NAMES. This is a narrower case than the fix this issue asks for. The general fix should also not default to linking: a new per-account file is safer kept local than shared.TimeAndLocation commentedon Oct 13, 2026
Windows reproduction: split WAL files can lose committed writes
Adding a data-loss reproduction for the sidecar-only variant already described here.
Environment: Windows 11 x64 (
10.0.26200), T3 Code Nightly0.0.46-nightly.20261013.3040, Codex CLI0.162.1, Node24.14.0. Two Codex accounts were configured with a shared home and a shadow home.In addition to provider-creation conflicts (
db-backupsin this installation), archived Codex databases failed SQLite integrity checks. Codex's retained logs explicitly reported corruption inthread_history_1.sqlite. The precise historical corruption timing was not captured, so the fixture below establishes a reproducible unsafe write mechanism rather than proving the origin of every damaged page.Reproduction
A fixture invoking T3's actual
materializeCodexShadowHomeimplementation from the installed server reproduced this sequence:-waland-shmfiles do not exist.Both inserts succeed, but only one of the two committed rows remains. The shadow connection uses its own regular WAL/SHM files for the linked base database. This does not require overlapping transactions, a crash, an authentication failure, or model inference.
Here is a standalone Node reproduction of the resulting file layout. Run as an
.mjsfile on Windows with file-symlink support. It uses only a fresh temporary directory:Observed: the assertion fails with
1 !== 2. The same write check with two independent physical provider databases retains both writes. The actual-T3 fixture also retained1/2with the shadow layout and2/2with independent homes.The relevant main-branch code still enumerates only entries currently present in the shared home: CodexHomeLayout.ts. SQLite explains why multiple names and separate journals/WAL files are unsafe.
An acceptance test should cover a linked base database whose sidecars were absent during materialization, then verify both committed writes survive. Handling an existing regular sidecar conflict alone would not establish database safety. Independent direct homes were used as the local workaround, preserving the account credentials and available rollouts; this does not claim to preserve the intended ongoing shared-history behavior of shadow homes.
Reproduction and diagnosis assisted by GPT-6.1-Sol in Codex desktop.
tgangso commentedon Oct 13, 2026
Follow-up to my earlier report: the providers became unavailable again on Windows, but this time with a different shadow-home failure mode.
Environment
0.0.46-nightly.20261013.3066(desktop, Nightly)0.162.1(verified with the CLI configured in T3)26200.9457, x64homePath(<user-home>/.codex), each with a separateshadowHomePath(<t3-userdata>/providers/codex/<account-instance>/shadow). Paths and account identifiers are placeholders.sqlite_homeoverride pointing to the shared Codex directory, withcli_auth_credentials_store="file".New findings
sqlite_homeoverride pointing to the shared Codex directory was still configured on all three affected providers.CodexShadowHomeFileSystemErrorwrappingEPERM: operation not permitted, symlink. T3 attempted to link a newly present, non-runtime configuration backup from the shared home into each shadow home. That single file blocked initialization of all three providers.memories_1.sqlite-shmandmemories_1.sqlite-wal.Verification and implication
All three affected providers subsequently showed Authenticated in T3, and the provider connection probes succeeded. The backup was preserved with its contents verified unchanged.
The
sqlite_homeoverride alone did not prevent T3's shadow-home initialization from requiring links for SQLite sidecars and other shared-home entries. This is a related Windows link-creation/permissions failure, distinct from the existing regular-file conflict reported earlier. It may warrant separate tracking at maintainers' discretion.This was a local recovery, not a verified permanent fix. No database-integrity testing was performed, and I am not claiming data loss or corruption in this installation. Personal paths, account details, and identifiers are omitted.